ShinyHunters exploiting workarounds for Oracle PeopleSoft bug, Mandiant warns
A vulnerability in a popular line of products from Oracle is being used in a new campaign by the prolific ShinyHunters hacking group, which recently claimed credit for an attack on the FBI’s jobs site.
The Google-owned security firm Mandiant published a blog on Friday about CVE-2026-35273 — a vulnerability disclosed in June that impacts Oracle’s PeopleSoft. PeopleSoft is used widely across government, education and healthcare for a variety of business tasks like managing invoices, projects and staffing.
Mandiant reported in June that ShinyHunters was exploiting the bug as a zero-day between May 27 and June 9 in attacks on academic institutions. Oracle eventually released a patch on June 10 and Mandiant provided guidance on how organizations could either install the patch or institute workarounds.
In its blog on Friday, Mandiant warned that ShinyHunters had restarted its exploitation of the bug and “adapted to published defensive guidance, targeting organizations that implemented [workarounds] but did not patch the vulnerability.”
“Our analysis indicates that the threat actor expanded their targeting in this recent campaign, deploying web shells on dozens of systems globally, spanning higher education, technology, IT services, healthcare, agriculture, transportation, and government,” Mandiant said.
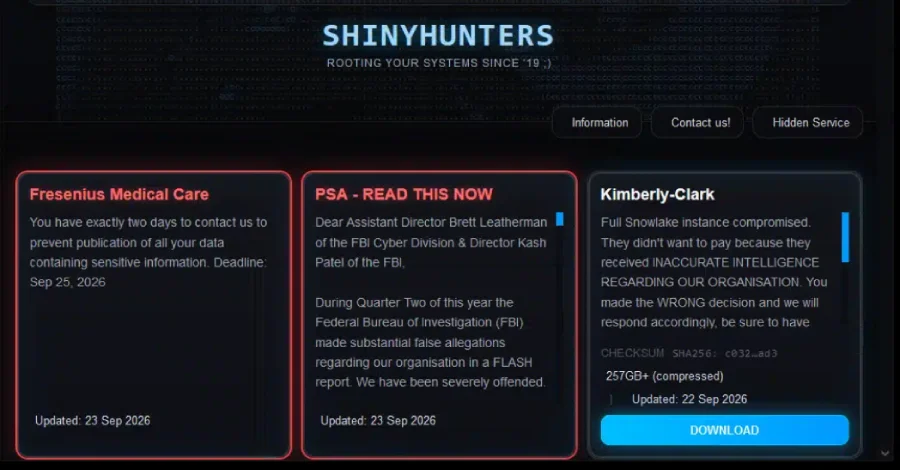
Last week, ShinyHunters took credit for an attack on the FBI that saw the group deface a jobs website run by the agency and allegedly steal troves of sensitive data on FBI operations and agents.
In a memo to FBI employees obtained by the New York Times, senior officials at the agency acknowledged the breach and said they are “operating under the premise that the threat actor is also exfiltrating [personal information] of all F.B.I. employees.”
On its website and in interviews with news outlets, ShinyHunters claimed it breached the FBI through a vulnerability in Oracle PeopleSoft — setting off a scramble to determine if the group found a new bug in the software or if it was exploiting a past issue.
Mandiant said it analyzed multiple compromised instances where the hackers were able to exploit the bug and pivot into obtaining full control of an operating system or at least gain access to PeopleSoft configuration files, database connection strings, and application data.
On its website, Oracle lists dozens of prominent PeopleSoft users that include government agencies across the U.S. and abroad, healthcare companies and universities. Mandiant urged all organizations to review database logs for any queries about human resources, payroll, and student records tables.
“[ShinyHunters] has a well-established pattern of data theft extortion, that is, stealing data and threatening to release it on a data leak site unless the victim pays a ransom,” Mandiant said. “Affected organizations should prepare for extortion communications and monitor for potential public exposure of stolen data.”
ShinyHunters has claimed dozens of high-profile attacks in recent months and has been in the crosshairs of the FBI for nearly a year after dozens of attacks on large companies like Ticketmaster and AT&T as well as educational publisher McGraw Hill, Carnival Cruise Line, 7-Eleven and other companies.
The group upped the ante last week with its attack on the FBI, providing 5,000-person samples of stolen data to numerous news outlets that confirmed the legitimacy of the data. Samples obtained by Reuters, 404 Media and the BBC contained sensitive medical records, information about secretive FBI units and detailed information on agents.
On Monday, Dutch police said they arrested a 24-year-old suspected member of ShinyHunters from Amsterdam. Cybersecurity reporter Brian Krebs reported the man was a key figure in the group and was locked in a power struggle with another hacker based in Jordan for control of the cybercriminal operation.
References in this story
- Oracle Security Alert Advisory - CVE-2026-35273 www.oracle.com Oracle Security Alert Advisory - CVE-2026-35273
- ShinyHunters Renewed Mass Exploitation Campaign Targeting Oracle PeopleSoft | Google Cloud Blog cloud.google.com This follow-up report details how UNC6240 (ShinyHunters) is mass-exploiting Oracle PeopleSoft (CVE-2026-35273) by bypassing WAF rules via a single URL-encoded character, providing full analysis of the attack pipeline…
- FBI investigating alleged ShinyHunters breach of its jobs site therecord.media The ShinyHunters cybercriminal organization on Tuesday replaced agency images on the FBIjobs.gov site with a photo of a Pokemon that has become the group’s defacto mascot.
- ShinyHunters claims FBI hack, data theft in PeopleSoft zero-day breach www.bleepingcomputer.com The ShinyHunters extortion gang claims it breached FBI systems using a new Oracle PeopleSoft zero-day vulnerability, gaining access to internal services and stealing sensitive data on employees and job applicants.
- PeopleSoft Innovators docs.oracle.com PeopleSoft Innovators have completed broad transformation initiatives in multiple strategic investment areas.
- Live Nation confirms Ticketmaster breach after hackers hawk stolen info of 560 million therecord.media The company has confirmed that the leaked data was from a database hosted on Snowflake — one of the largest cloud storage companies.
- Hackers stole ‘nearly all’ call logs over six months from AT&T therecord.media The telecom giant said the massive breach involving logs from 2022 occurred through the third-party cloud platform Snowflake.
- Educational company McGraw Hill says Salesforce misconfiguration led to data leak therecord.media The data breach emerged this weekend when the ShinyHunters cybercriminal organization claimed to have stolen 45 million Salesforce records and threatened to leak the information by April 14 if a ransom was not paid.
- Cruise giant Carnival confirms data breach affecting nearly 6 million people therecord.media The company said the threat actor gained access to a limited portion of its IT environment last month after compromising an employee account. By the end of April, Carnival determined that the attacker had copied…
- 7-Eleven confirms breach after ShinyHunters claims therecord.media The breach notification letters say 7-Eleven discovered the breach on April 8 and, after an investigation, determined that the cybercriminals gained access to “certain 7-Eleven systems used to store franchisee…
- ADT says customer data stolen in cyber intrusion therecord.media The home security company ADT said cybercriminals breached company systems on Monday and stole a “limited set” of customer and prospective customer information.
- Hackers claim breach of Rockstar Games via cloud analytics platform therecord.media The ShinyHunters cybercrime group has claimed responsibility for breaching systems linked to video game developer Rockstar Games, threatening to release stolen data if a ransom is not paid.
- FBI Hack Exposed FBI’s Own Hacking Unit www.404media.co The FBI's Remote Operations Unit (ROU) is a highly secretive team of hackers making exploits and tools to break into target’s devices. Some of its members just got exposed.
- Special agents blood and urine test results stolen in FBI hack www.bbc.com Experts say the hack could leave agents vulnerable to scams, blackmail and targeted attacks.
- Politie Landelijke Opsporing en Interventies (@Pol_Ops_Int) on X x.com Het klopt dat er deze maand een 24-jarige man uit Amsterdam is aangehouden in een onderzoek naar de hackersgroep ShinyHunters. Op dinsdag 29 september staat de man voor de raadkamer van de rechtbank Rotterdam. Morgen…
- Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation – Krebs on Security krebsonsecurity.com
- Meet Rey, the Admin of ‘Scattered Lapsus$ Hunters’ – Krebs on Security krebsonsecurity.com
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- jon greig (@jgreigj) on X twitter.com @TheRecord_Media cybersecurity reporter. formerly @zdnet @cambodiadaily @haitiantimes_ — send tips to [email protected] or signal: jgreig.51
- jon greig (@jgreig.bsky.social) bsky.app cybersecurity reporter for The Record. formerly: zdnet, techrepublic, blavity, haitian times, cambodia daily — send tips to [email protected] or signal: jgreig.51