FBI investigating alleged ShinyHunters breach of its jobs site
The Federal Bureau of Investigation is investigating a breach of its job applications platform after a cybercriminal group defaced the website and claimed to have stolen information on current and former employees and applicants.
The ShinyHunters cybercriminal organization on Tuesday replaced agency images on the FBIjobs.gov site with a photo of a Pokemon that has become the group’s defacto mascot.
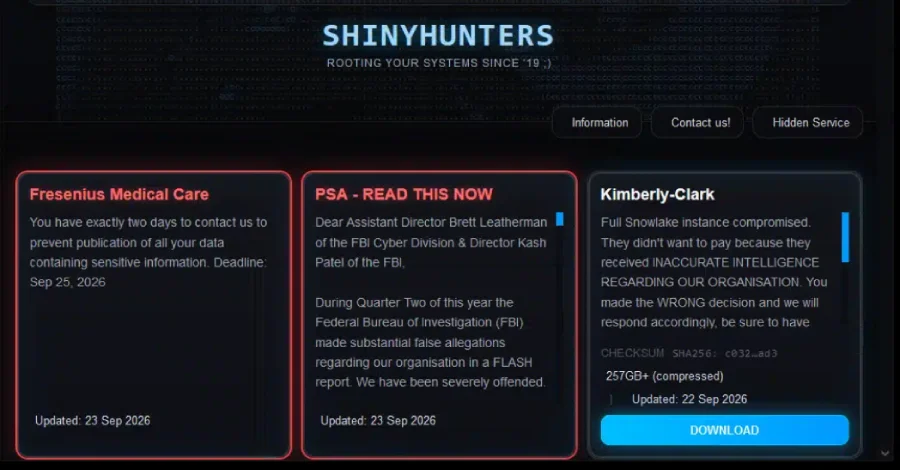
The group then took to its leak site to post a lengthy statement criticizing the FBI for a public service announcement released earlier this year that made several assertions ShinyHunters’ claims are false. The group threatened to leak information on every FBI agent and anyone who has applied for a job at the FBI if the white notice was not taken down.
“The FBI is aware of claims regarding unauthorized activity affecting FBIjobs.gov and is currently investigating,” an FBI spokesperson told Recorded Future News on Tuesday evening. The agency did not respond to several other questions about the claims made by ShinyHunters.
As of Wednesday morning, the FBI jobs site still has a banner saying the special agent application portal is currently unavailable.
ShinyHunters provided samples of 5,000 stolen FBI agent records to 404media and several other news outlets, which confirmed their legitimacy.
In its message yesterday, ShinyHunters took issue with FBI claims that it exaggerated the data it stole and that it extorted the employees of the companies they hacked into.
"We wish to state unequivocally we have never conducted swatting attacks against corporate victims personnel nor have we ever texted victims personnel family members any threats,” the group claimed. “We wish to state unequivocally we have never claimed to have sensitive information, including embarrassing photographs and videos of victims. We are not sextortionists.”
The group also denied being part of The Com — a larger group of young English-speaking hackers accused of various crimes targeting children online.
The notice was issued by the FBI in May following ShinyHunters attack on educational software giant Instructure. The attack disrupted operations at thousands of universities and K-12 schools across the U.S., forcing the company to eventually pay the ransom to restore its services.
The group has been in the crosshairs of the FBI for nearly one year after dozens of high-profile attacks on large companies like Ticketmaster and AT&T as well as educational publisher McGraw Hill, Carnival Cruise Line, 7-Eleven and other companies.
Brett Leatherman, assistant director of the FBI’s Cyber Division, spoke at length about the group during a roundtable two weeks ago, telling reporters that after successfully securing the arrest of members of a related cybercriminal group, the FBI is now “focused” on ShinyHunters “because right now it's a big problem when it comes to data exfiltration and extortion attacks.”
Several experts said it is likely the group will leak the stolen data because the FBI will not remove the alert.
“The bigger worry is ShinyHunters selling the data to other criminal or nation-state groups who could put it to more damaging use, rather than dumping it themselves,” said Andrew Brandt, incident responder at cybersecurity firm Huntress.
“These are law enforcement personnel who deal with serious and dangerous criminals, sometimes requiring infiltration into criminal networks. It could be abused in a multitude of ways, from financial fraud to serious threats of harm against staff and their immediate families, to future targeted attacks in cyberspace or the physical world.”
Additional reporting by Martin Matishak.
References in this story
- Internet Crime Complaint Center (IC3) | ShinyHunters: Cyber Criminal Group Attacks Learning Management System www.ic3.gov
- ‘We Hacked the FBI:’ Hackers Say They Have Data on All FBI Employees www.404media.co A sample of 5,000 alleged agents seen by 404 Media includes names, addresses, phone numbers, and details on FBI employees' spouses.
- Instructure pays ransom after Canvas incident as Congress announces investigation therecord.media The company said its agreement with the hackers involved their data being “returned” to them and digital confirmation of data destruction.
- Live Nation confirms Ticketmaster breach after hackers hawk stolen info of 560 million therecord.media The company has confirmed that the leaked data was from a database hosted on Snowflake — one of the largest cloud storage companies.
- Hackers stole ‘nearly all’ call logs over six months from AT&T therecord.media The telecom giant said the massive breach involving logs from 2022 occurred through the third-party cloud platform Snowflake.
- Educational company McGraw Hill says Salesforce misconfiguration led to data leak therecord.media The data breach emerged this weekend when the ShinyHunters cybercriminal organization claimed to have stolen 45 million Salesforce records and threatened to leak the information by April 14 if a ransom was not paid.
- Cruise giant Carnival confirms data breach affecting nearly 6 million people therecord.media The company said the threat actor gained access to a limited portion of its IT environment last month after compromising an employee account. By the end of April, Carnival determined that the attacker had copied…
- 7-Eleven confirms breach after ShinyHunters claims therecord.media The breach notification letters say 7-Eleven discovered the breach on April 8 and, after an investigation, determined that the cybercriminals gained access to “certain 7-Eleven systems used to store franchisee…
- ADT says customer data stolen in cyber intrusion therecord.media The home security company ADT said cybercriminals breached company systems on Monday and stole a “limited set” of customer and prospective customer information.
- Hackers claim breach of Rockstar Games via cloud analytics platform therecord.media The ShinyHunters cybercrime group has claimed responsibility for breaching systems linked to video game developer Rockstar Games, threatening to release stolen data if a ransom is not paid.
- Two Scattered Spider members plead guilty over cyberattack that crippled London transit therecord.media A 20-year-old and an 18-year-old admitted to infiltrating the network of Transport for London in 2024, disrupting public transportation services for months.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- jon greig (@jgreigj) on X twitter.com @TheRecord_Media cybersecurity reporter. formerly @zdnet @cambodiadaily @haitiantimes_ — send tips to [email protected] or signal: jgreig.51
- jon greig (@jgreig.bsky.social) bsky.app cybersecurity reporter for The Record. formerly: zdnet, techrepublic, blavity, haitian times, cambodia daily — send tips to [email protected] or signal: jgreig.51