ShinyHunters Claims FBI Breach, Data Stolen
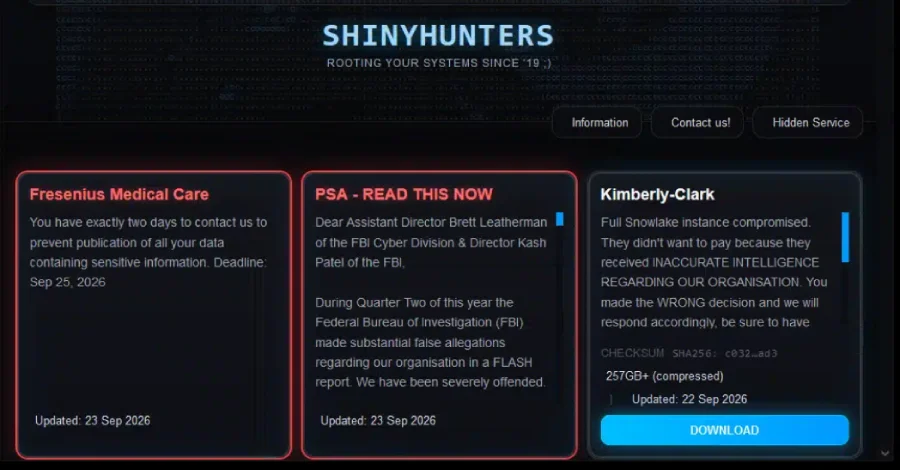
ShinyHunters claims it breached the FBI and stole sensitive data, while the bureau investigates a confirmed compromise of its jobs portal.
The cybercriminal group ShinyHunters claims it breached the U.S. Federal Bureau of Investigation and stole sensitive information belonging to FBI employees, former employees and people who applied for jobs with the agency.
The FBI has confirmed that its FBIJobs.gov portal was compromised and that it is investigating the incident. However, the bureau has not confirmed that its internal enterprise network was breached or that all of the data claimed by ShinyHunters was obtained from FBI systems.
In a statement released on September 23, the FBI said it was aware of a cybercriminal group’s claims regarding the compromise of FBIJobs.gov and alleged impact to employee personally identifiable information. The bureau said the point of the breach remains undetermined and could involve either a third-party provider supporting FBIJobs.gov or the FBI’s own enterprise environment.
ShinyHunters said it had obtained highly sensitive information on almost all FBI agents as well as people who had submitted job applications to the bureau.
The group claimed that several FBI-related services had been compromised, including systems associated with criminal justice, human resources and Medlink.
ShinyHunters also claimed that the operation was carried out using a previously unknown vulnerability in Oracle PeopleSoft, allowing the attackers to obtain remote code execution and subsequently compromise the FBI’s recruitment infrastructure.
That particular attack path has not been independently confirmed.
The Hacker News reported that there is currently no publicly documented PeopleSoft pre-authenticated remote-code-execution vulnerability matching ShinyHunters’ description. The group did previously exploit a separate PeopleSoft vulnerability, CVE-2026-35273, during a campaign against enterprise organizations earlier this year.
One part of the incident is now confirmed.
The FBI has acknowledged that FBIJobs.gov was compromised and said it is working with third-party providers supporting the recruitment system to investigate and mitigate the incident. The bureau has not yet determined whether the compromise originated with one of those providers or within the FBI’s own enterprise environment.
The FBI’s recruitment infrastructure includes FBIJobs.gov and a separate Candidate Gateway used for job applications.
An FBI privacy impact assessment also shows that the recruitment system uses Oracle PeopleSoft to store application data and is hosted on Amazon Web Services GovCloud. The system can contain sensitive applicant information including names, Social Security numbers and dates of birth.
This does not establish that those particular records were stolen in the ShinyHunters incident, but it explains why the alleged compromise has attracted significant attention.
ShinyHunters provided journalists with a sample that it claimed contained information on approximately 5,000 FBI personnel.
Reuters reviewed the sample and found information that appeared to correspond to real FBI employees, including names, home addresses, Social Security numbers and work assignments. In at least some cases, information about family members was also present.
Reuters was able to partially verify information in at least 10 cases by comparing the records against credit bureau information and previously compromised data. However, the publication could not determine where the information originally came from or independently establish that it had been stolen directly from FBI systems.
That distinction is important.
The sample provides evidence that at least some of the information is genuine, but it does not independently prove ShinyHunters’ much broader claim that it obtained data on almost all FBI agents and applicants.
If the information is authentic and was obtained through the compromised recruitment infrastructure, the potential exposure goes beyond ordinary applicant information.
The reported sample contains personal details such as names, addresses, telephone numbers and Social Security numbers. Some records reportedly also contain employment assignments and information about relatives.
Exposure of information connecting specific FBI employees to particular assignments could create additional security concerns, particularly where personnel work in sensitive investigative or intelligence roles.
At this stage, however, the full extent of any exposure remains unknown.
ShinyHunters said the FBI was targeted in response to a May 2026 public service announcement in which the bureau warned organizations about the group’s activities and advised victims against paying its demands.
The group accused the FBI of making false claims about its activities and demanded that the bureau retract or correct the earlier warning.
ShinyHunters has also rejected claims linking it to the broader decentralized hacking collective known as The Com. These statements represent the group’s own characterization of the incident and have not been independently established.
What Is Confirmed So Far?
Several parts of the incident can now be separated from the group’s broader claims.
The FBIJobs.gov portal was compromised.
The FBI is investigating the incident.
The bureau has not yet determined the point of compromise.
ShinyHunters has claimed responsibility and says it obtained extensive FBI-related data.
A sample supplied by the group contains information that appears to correspond to real FBI personnel, with Reuters independently verifying portions of the information.
What remains unconfirmed is how the data was obtained, whether it came directly from FBI systems, the total amount of information accessed, and whether ShinyHunters actually obtained data belonging to almost all FBI agents and applicants.
The claimed PeopleSoft zero-day attack path also remains unverified.
For now, the incident is best described as a confirmed compromise of the FBI’s public-facing recruitment infrastructure combined with an alleged large-scale theft of FBI-related data that is still under investigation.
As the FBI works to determine the source and scope of the compromise, ShinyHunters is threatening to release additional information if its demands are not met.
Source: The Hacker News
References in this story
- ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants thehackernews.com ShinyHunters claims it breached the FBI and stole employee data; the bureau says it is investigating activity affecting FBIjobs.gov.