Pharmaceutical giant McKesson warns of 'service degradation' following cyberattack
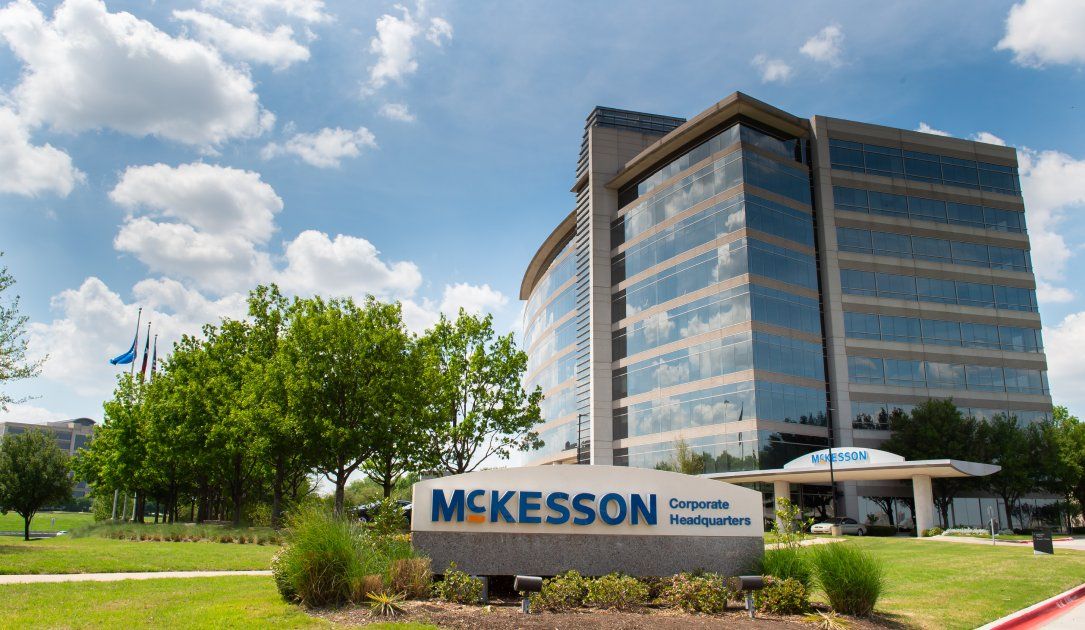
A cyberattack is causing service issues for the pharmaceutical and healthcare technology company McKesson.
The company released a public notice and filed documents with the Securities and Exchange Commission (SEC) on Friday evening saying it is in the early stages of investigating a cybersecurity incident that involves an unnamed third-party application.
The hackers have gained access to the application and are exfiltrating data, McKesson said.
“At this time, customers may experience intermittent service degradation that we believe may be related to this incident,” McKesson chief technology officer Francisco Fraga said in a statement. “We are aware of these issues and continue to monitor the situation closely.”
In an update on Saturday, the company said the hackers exfiltrated data associated with customers in their oncology and surgical business units. Fraga said they will provide credit monitoring and identity protection services to customers whose data was exfiltrated.
They have also received “reasonable assurance” that the hackers are no longer inside McKesson systems.
“Customers can continue to connect to and use our systems and services as intended,” Fraga explained.
He noted that it is not proactively disconnecting systems — an action typically taken during ransomware attacks to limit the reach of attackers and contain the blast radius of the incident.
He urged customers to contact the company if there are technical issues with services. McKesson said it is still in the midst of an investigation and did not answer questions about the incident when reached for comment.
The ShinyHunters cybercriminal group took credit for the attack on Friday night, threatening the company with potential leaks in a post on their blog. The group has spent more than two years attacking and extorting some of the largest companies in the world.
Earlier this year, the FBI warned that hackers linked to ShinyHunters were demanding substantial ransom payments from companies after stealing data through compromises involving Salesforce environments.
The group caused chaos across the U.S. in May with an attack on a widely used educational software suite and stole the information of more than four million people after attacking the world’s largest medical device company in April.
Other victims include Carnival Cruises, Ticketmaster, AT&T, McGraw Hill and ADT and gaming company Rockstar.
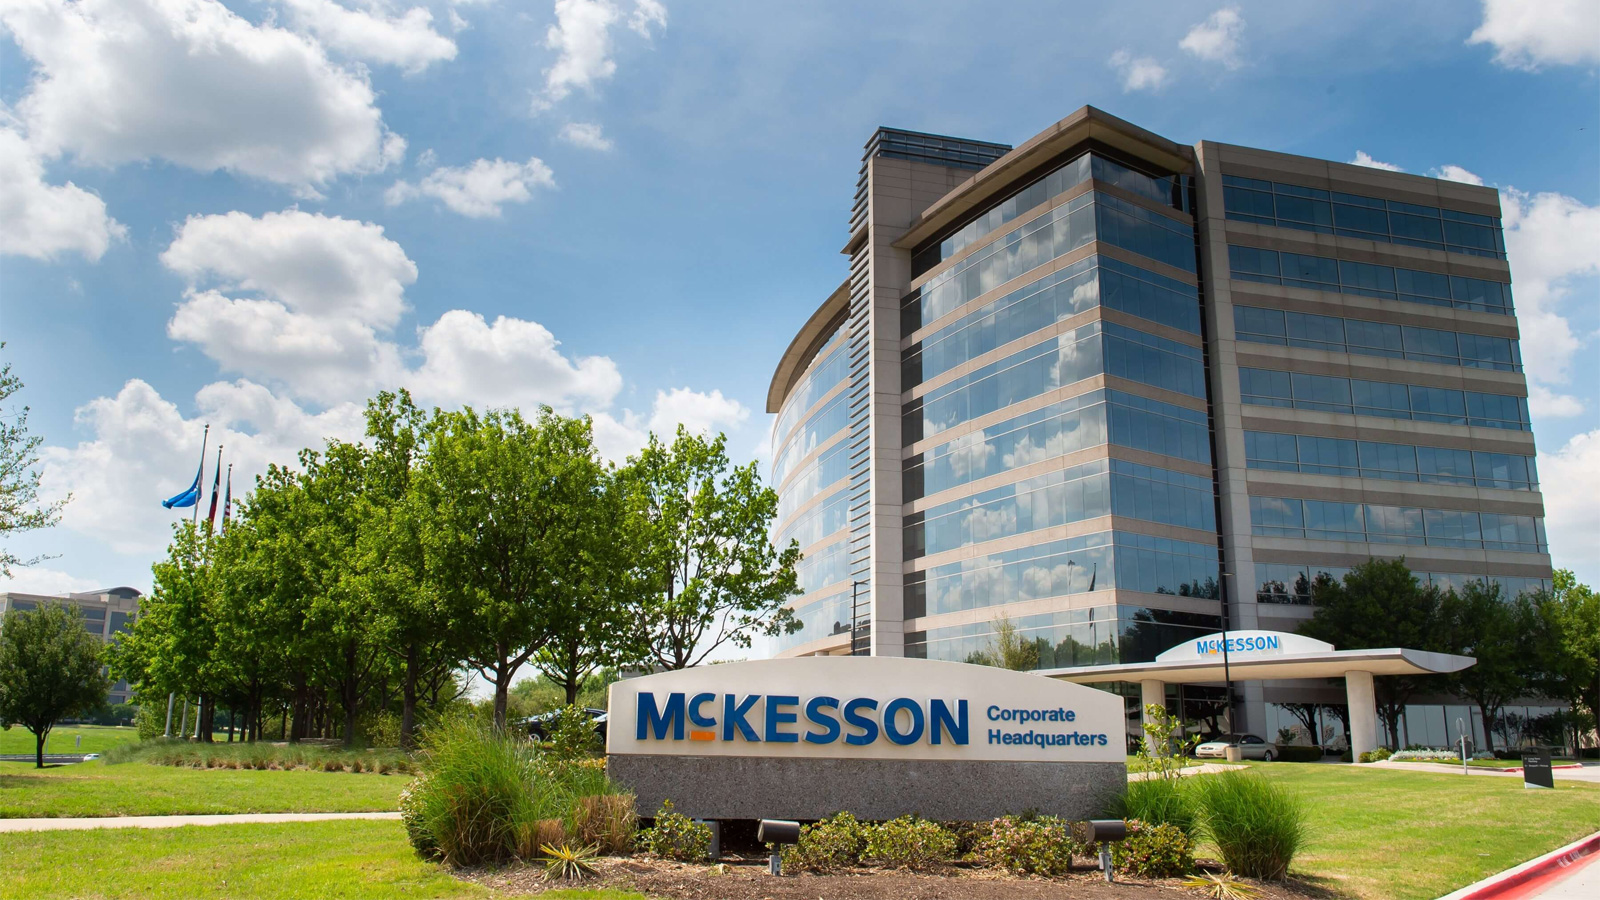
McKesson reported $106 billion in revenue last quarter. About one-third of all prescriptions in North America are delivered by the company.
The Texas-based company distributes pharmaceuticals, produces drugs for oncology patients, and manufactures a range of critical medical-surgical supplies, laboratory equipment and more.
McKesson is the latest large healthcare company to be attacked this year after medical device giants Boston Scientific and Medtronic both reported cybersecurity incidents. Another large medical device firm, Stryker, was also hit with a cyberattack earlier this year.
References in this story
- Customer Cybersecurity Information Center www.mckesson.com
- Dark Web Informer (@DarkWebInformer) on X x.com ‼️🇺🇸🇸🇪 ShinyHunters claims McKesson and Elekta AB. 🇺🇸 McKesson Corporation - A U.S.-based healthcare company providing pharmaceutical distribution, medical supplies, healthcare technology, and related services. The…
- FBI warns of Scattered Spider and ShinyHunters attacks on Salesforce platforms therecord.media The FBI released an urgent notice warning organizations about a campaign by several cybercriminal groups to compromise Salesforce platforms.
- Instructure pays ransom after Canvas incident as Congress announces investigation therecord.media The company said its agreement with the hackers involved their data being “returned” to them and digital confirmation of data destruction.
- Major medical device manufacturer notifies nearly 4 million of breach therecord.media Information like Social Security numbers and health-related data was accessed, but the company said it had “no evidence that impacted information has been publicly posted or exposed on the internet.”
- Cruise giant Carnival confirms data breach affecting nearly 6 million people therecord.media The company said the threat actor gained access to a limited portion of its IT environment last month after compromising an employee account. By the end of April, Carnival determined that the attacker had copied…
- Live Nation confirms Ticketmaster breach after hackers hawk stolen info of 560 million therecord.media The company has confirmed that the leaked data was from a database hosted on Snowflake — one of the largest cloud storage companies.
- Hackers stole ‘nearly all’ call logs over six months from AT&T therecord.media The telecom giant said the massive breach involving logs from 2022 occurred through the third-party cloud platform Snowflake.
- Educational company McGraw Hill says Salesforce misconfiguration led to data leak therecord.media The data breach emerged this weekend when the ShinyHunters cybercriminal organization claimed to have stolen 45 million Salesforce records and threatened to leak the information by April 14 if a ransom was not paid.
- ADT says customer data stolen in cyber intrusion therecord.media The home security company ADT said cybercriminals breached company systems on Monday and stole a “limited set” of customer and prospective customer information.
- Hackers claim breach of Rockstar Games via cloud analytics platform therecord.media The ShinyHunters cybercrime group has claimed responsibility for breaching systems linked to video game developer Rockstar Games, threatening to release stolen data if a ransom is not paid.
- Medical device firm Boston Scientific says cyberattack has disrupted shipment processes therecord.media The company released a statement and filed documents with the Securities and Exchange Commission (SEC) saying a cybersecurity incident was discovered on Tuesday.
- Stryker tells SEC that timeline for recovery from cyberattack unknown therecord.media In an 8-K filing with the SEC, Stryker confirmed that the cyberattack caused a global disruption to the company’s Microsoft environment and said external cybersecurity experts were brought in to “assess and to contain…
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- jon greig (@jgreigj) on X twitter.com @TheRecord_Media cybersecurity reporter. formerly @zdnet @cambodiadaily @haitiantimes_ — send tips to [email protected] or signal: jgreig.51
- jon greig (@jgreig.bsky.social) bsky.app cybersecurity reporter for The Record. formerly: zdnet, techrepublic, blavity, haitian times, cambodia daily — send tips to [email protected] or signal: jgreig.51