Microsoft takes down 3 major phishing platforms used by Chinese cybercriminals
Microsoft on Wednesday announced legal action disrupting three powerful phishing platforms used by Chinese cybercriminals to send hundreds of millions of malicious messages impersonating over 75,000 organizations worldwide.
The tech giant worked with Japan’s National Police Agency and healthcare cybersecurity organization Health-ISAC to obtain a U.S. court order seizing and redirecting domains that were part of the infrastructure underlying YAM Store, CoGUI and Iron Man.
Since January, the three platforms collectively enabled more than 750 million messages targeting Microsoft customers alone.
These messages have been used to target consumers, healthcare organizations, financial institutions and other businesses in more than 150 countries, generating tens of millions of dollars for their operators. The goal of most of the tools is to steal credentials, personal information, banking data and other login information.
Iron Man is a phishing-kit-as-a-service operation that offers cybercriminals more than 2,300 pre-built lure pages impersonating trusted services like postal companies, traffic fine offices, tax agencies, banks, telecoms and more. Iron Man’s customers purchase a subscription that offers thousands of templates tailored for Australia, Japan, India and dozens of other countries.
CoGUI provides criminals with ready-made websites and messages that can impersonate trusted brands, companies, government agencies and financial institutions.
CoGUI was used heavily to target people in Japan but cybercriminals began shifting to Iron Man by the middle of 2026. In addition to the templates allowing criminals to impersonate brands, Iron Man allowed thieves to “quickly deploy email, text and web content tailored to specific brands, industries and countries.”
Steven Masada, associate general counsel for Microsoft's Digital Crimes Unit, said the investigation into the sites began last year when Japanese police officials flagged messaging campaigns targeting people in Japan.
The campaigns were traced back to a Chinese-language cybercrime ecosystem that began with CoGUI but quickly expanded beyond the site. As Microsoft and Japanese officials tied multiple scam campaigns to the same infrastructure, they were led to YAM Store.
YAM Store is an initial access broker marketplace that “sells infrastructure using compromised or fraudulently obtained environments in providers like Microsoft and Google,” Microsoft researchers explained. It allowed cybercriminals to effectively browse for the cheapest fraudulent Microsoft and Google accounts that would enable their scams.
“The marketplace offers a variety of infrastructure based on age, subscription type, and environment types such as education (.edu) or non-profit (.org),” Microsoft explained, noting that cybercriminals could purchase domains tied to legitimate or expired organization names.
Cybercriminals bought internet domains that real companies had allowed to expire, rebuilding websites to look like legitimate platforms. The sites could be used to steal Microsoft 365 credentials that could then be sold for money on YAM Store.
With the court order, Microsoft was able to seize and redirect the domains while also disabling more than 20,000 accounts connected to YAM Store. Microsoft said it is still removing infrastructure hosted on its services and is blocking more than 100,000 domains used for impersonation.
Microsoft noted that it shared information with U.S. and international law enforcement partners and worked with cybersecurity firm Resecurity to infiltrate the sites.
Masada explained in a blog post that the tools are the driving force behind many of the toll scam texts or fake delivery emails people are inundated with on a daily basis.
The investigation revealed similarities between the infrastructure of YAM Store, CoGUI and Iron Man, indicating close collaboration among their developers or shared development origins.
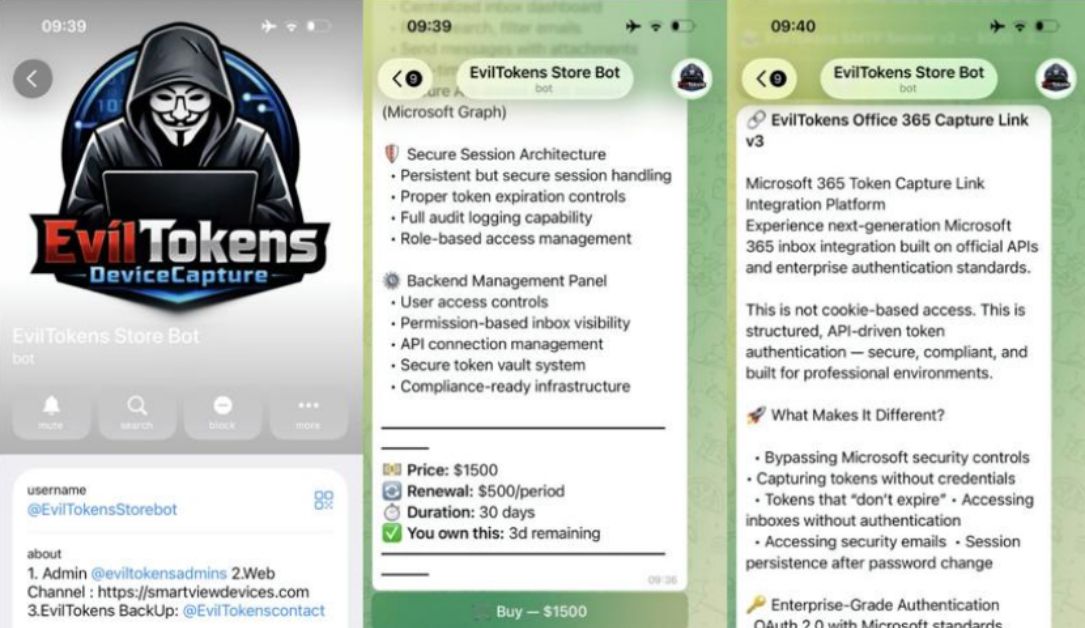
Microsoft has ramped up its use of the legal system to take down phishing platforms designed to steal Microsoft credentials. Last month, it took legal action against an AI-powered cybercriminal platform called EvilTokens — using court authorization to take the tool offline and work with police in the U.K. to arrest those allegedly behind it.
Microsoft dismantled hundreds of servers and domains in June that were tied to cybercrime-as-a-service infrastructure belonging to cybercriminal gangs distributing SocGholish, Amadey and StealC malware. The company previously targeted other popular cybercriminal phishing platforms like RaccoonO365 and RedVDS over the last year.
References in this story
- Two arrested in UK after Microsoft takedown of ‘Eviltokens’ AI-chatbot for cybercriminals therecord.media Available on Telegram for a $1,500 initiation fee and a recurring monthly $500 subscription, EvilTokens provided cybercriminals with artificial intelligence tools enabling them to compromise accounts, analyze breached…
- Three ‘cybercrime as a service’ operations undercut by Microsoft, law enforcement therecord.media Microsoft touted its latest action against malware infrastructure as a new approach aimed at the full cybercrime "supply chain." Europol said more than 300 servers were targeted.
- Microsoft, Cloudflare disrupt RaccoonO365 credential stealing tool run by Nigerian national therecord.media Microsoft found that the group behind RaccoonO365 has been paid at least $100,000 in cryptocurrency from about 100 subscriptions. This is likely only a portion of the money earned from the tool, according to Microsoft.
- Microsoft disrupts RedVDS cybercrime platform behind $40 million in scam losses therecord.media Microsoft and law enforcement partners took down a popular cybercriminal subscription service called RedVDS that was used to enable more than $40 million in fraud losses in the United States alone.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- jon greig (@jgreigj) on X twitter.com @TheRecord_Media cybersecurity reporter. formerly @zdnet @cambodiadaily @haitiantimes_ — send tips to [email protected] or signal: jgreig.51
- jon greig (@jgreig.bsky.social) bsky.app cybersecurity reporter for The Record. formerly: zdnet, techrepublic, blavity, haitian times, cambodia daily — send tips to [email protected] or signal: jgreig.51