Hundreds of thousands impacted by data breach at biosensor firm iRhythm
Medical device maker iRhythm said the data of at least 360,000 people was breached in a June cyberattack.
The company began filing breach notices in multiple states this week, telling regulators and victims that the incident occurred on June 8 and involved unauthorized access to third-party systems.
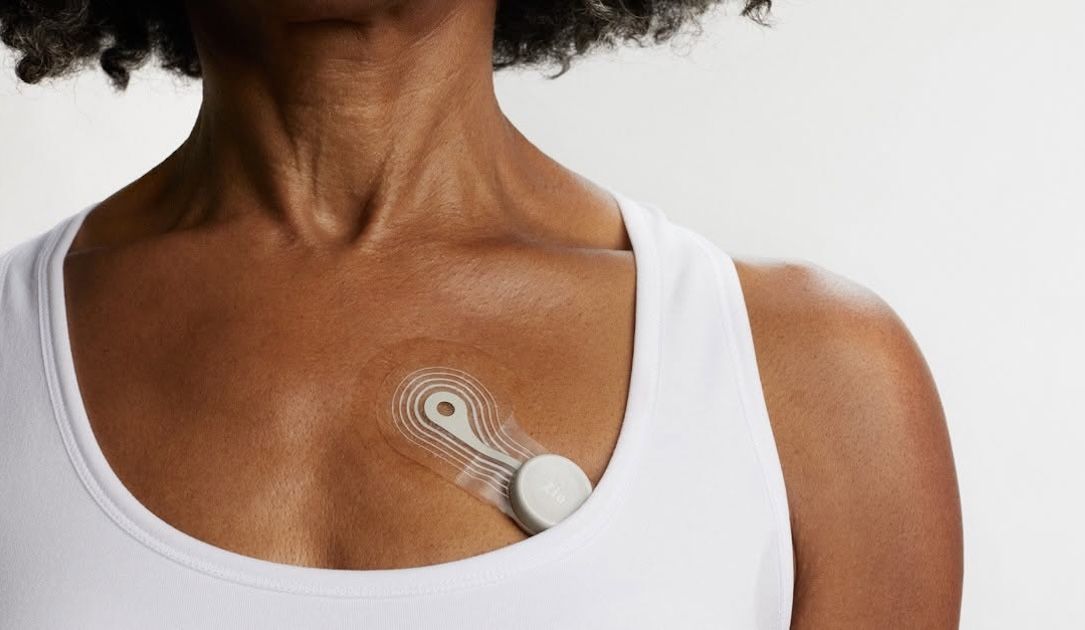
iRhythm is best known for Zio Patch — a sensor that patients wear on their chest for long-term continuous cardiac monitoring and heart arrhythmia detection.
The company said 298,647 people in Texas had information stolen alongside another 69,526 in South Carolina. iRhythm also filed breach notices in California.
A company spokesperson declined to say the full number of victims, telling Recorded Future News that iRhythm “responded promptly after detecting the unauthorized access and, once the scope was verified, notified affected individuals and applicable regulators.”
“The incident did not affect iRhythm clinical systems or medical devices and did not result in a loss of service or disruption to operations,” the spokesperson said.
An investigation into the incident revealed that hackers had access to company systems between June 3 and June 8. The hackers gained access to unidentified third-party-hosted business applications through a social engineering attack.
The information stolen includes names, addresses, phone numbers, iRhythm patient account numbers, iRhythm device serial numbers, patient insurance numbers, dates of service, and date of birth.
The cybercriminals accessed and downloaded the information, according to a statement from iRhythm. The company said it has “no evidence that any personal information has been or will be used to commit identity theft.” No hacking group ever publicly took credit for the attack.
The cyberattack did not impact the company’s products, devices, manufacturing process or distribution operations — and iRhythm said its finances were not disturbed. The company reported $224.2 million in Q2 revenue.
In a June 8-K filing with the Securities and Exchange Commission (SEC), iRhythm said it “received communications from a threat actor claiming to have obtained sensitive information, including proprietary data, patient protected health information and other personal information.”
“The communications from the threat actor demanded payment in exchange for not publicly disclosing this information,” the company said.
“Since receipt of the communications, the Company has confirmed that certain data was exfiltrated from those applications.”
Medical device companies have been battered by cybercriminals over the last two years, with dozens experiencing cybersecurity incidents that impacted crucial business and manufacturing systems.
Cyberattacks on Medtronic, Boston Scientific, Stryker, UFP, Masimo, Surmodics, Artivion and Zoll have leaked the sensitive medical data of millions and caused supply chain issues.
References in this story
- Submitted Breach Notification Sample oag.ca.gov
- Major medical device manufacturer notifies nearly 4 million of breach therecord.media Information like Social Security numbers and health-related data was accessed, but the company said it had “no evidence that impacted information has been publicly posted or exposed on the internet.”
- Medical device firm Boston Scientific says cyberattack has disrupted shipment processes therecord.media The company released a statement and filed documents with the Securities and Exchange Commission (SEC) saying a cybersecurity incident was discovered on Tuesday.
- Medical device giant Stryker confirms cyberattack as employees say devices were wiped therecord.media The medical device manufacturer Stryker confirmed reports Wednesday that a cyberattack has disrupted operations after a hacker group claimed to have targeted the company in retaliation for U.S. and Israeli strikes on…
- Medical device firm UFP says backup data systems deployed following cyberattack therecord.media In a filing with U.S. regulators, Massachusetts-based medical device manufacturer UFP Technologies said intruders possibly stole or destroyed company data during an incident earlier in February.
- Medical device giant Masimo says cyberattack is limiting ability to fill customer orders therecord.media California-based Masimo, known for oximeters and other medical devices, reported that a late April cyberattack has temporarily limited its ability "to process, fulfill, and ship customer orders."
- Medical device company Surmodics reports cyberattack, says it’s still recovering therecord.media Surmodics, a Minnesota-based company that makes specialized coatings for medical devices, reported a cyberattack to federal regulators.
- Medical device company says shipping processes disrupted by ransomware attack therecord.media Atlanta-based Artivion filed documents with the Securities and Exchange Commission saying that a pre-Thanksgiving ransomware attack was disrupting its delivery systems.
- Medical device giant says cyberattack leaked sensitive data of 1 million people therecord.media Medical device maker Zoll said a cyberattack in January exposed the sensitive information of more than 1 million people.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- jon greig (@jgreigj) on X twitter.com @TheRecord_Media cybersecurity reporter. formerly @zdnet @cambodiadaily @haitiantimes_ — send tips to [email protected] or signal: jgreig.51
- jon greig (@jgreig.bsky.social) bsky.app cybersecurity reporter for The Record. formerly: zdnet, techrepublic, blavity, haitian times, cambodia daily — send tips to [email protected] or signal: jgreig.51