ShinyHunters cybercrime gang takes over Cl0p ransomware site, demands extortion payment
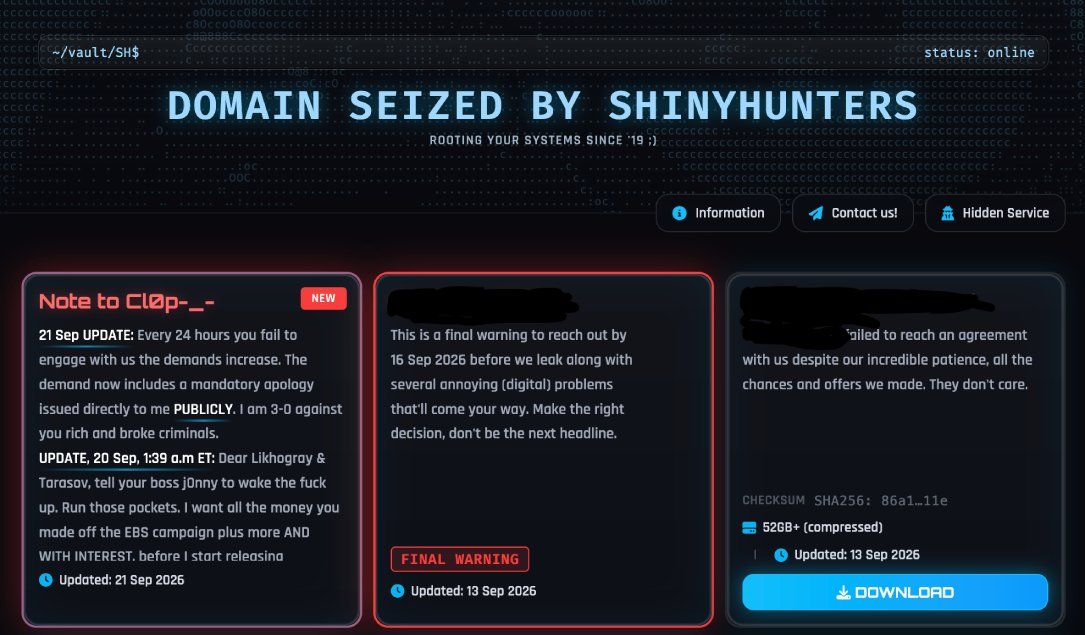
The ShinyHunters extortion group hijacked the dark web leak site of the prolific Cl0p ransomware gang, according to material posted on the site over the weekend.
The site, which Cl0p has used for years to name its hacking victims and pressure them into making an extortion payment, was used for those purposes against Cl0p itself.
It was defaced with a banner saying the domain had been seized by ShinyHunters, a group better known for social engineering and data extortion than technical hacking.
In messages posted on the site purportedly from ShinyHunters, the group set an unspecified eight-figure extortion demand and described that amount as “2.333%” of their own net worth, implying self-claimed holdings of at least hundreds of millions of dollars.
“I hope you can pay that much because that is the demand, negotiable. Get your bosses in front of the white board in the war room. Clock is ticking moron. Kindly excuse our unprofessionalism,” the notice said.
The hackers claimed their demands would increase every 24 hours that Cl0p failed to respond. By Monday, the demands had expanded to include a public apology from Cl0p.
A message posted Sunday named three people identified as Cl0p operators, all of whom have previously been named in public reporting. It also demanded proceeds from Cl0p’s recent campaign targeting Oracle’s E-Business Suite, “plus more.”
“Be sure to bring an English interlocutor so you can comprehend my literacy in acquiring your bank account,” the message stated.
The attacks on E-Business Suite, a widely used business platform, prompted warnings from Oracle, the FBI and cybersecurity agencies in the United Kingdom and Singapore.
The campaign followed ShinyHunters’ public release of a proof-of-concept exploit for the Oracle vulnerability on Telegram. ShinyHunters said its feud with Cl0p stems from the ransomware group’s unauthorized use of the vulnerability and threats against one of its members.
As part of the extortion attempt, the cybercriminals are threatening to release records showing which companies paid Cl0p, how much they paid and which Bitcoin addresses were used.
The defaced site was replaced on Monday by a message apparently from Cl0p, stating: “Shiny Hunters we trying to reach you Your email does not work. Come online old platform no email[.]”
ShinyHunters disrupted schools across the U.S. in May with an attack on a widely used education platform and stole information belonging to more than 4 million people in an April attack on the world’s largest medical device company.
Other victims have included Carnival Cruise Line, Ticketmaster, AT&T, McGraw Hill, ADT and gaming company Rockstar.
Cl0p is believed to have earned hundreds of millions of dollars by exploiting previously unknown vulnerabilities in widely used file-transfer products, including those from Cleo, MOVEit, GoAnywhere and Accellion.
Correction: An earlier version of this story incorrectly described the “2.333%” claim as reflecting Cl0p’s net worth. The figure was from the ShinyHunters author describing their own net worth.
References in this story
- FBI, UK gov’t urge orgs to patch Oracle E-Business vuln after alleged Clop campaign therecord.media FBI Assistant Director Brett Leatherman said “this is ‘stop-what-you’re-doing and patch immediately’ vulnerability.”
- Instructure pays ransom after Canvas incident as Congress announces investigation therecord.media The company said its agreement with the hackers involved their data being “returned” to them and digital confirmation of data destruction.
- Major medical device manufacturer notifies nearly 4 million of breach therecord.media Information like Social Security numbers and health-related data was accessed, but the company said it had “no evidence that impacted information has been publicly posted or exposed on the internet.”
- Cruise giant Carnival confirms data breach affecting nearly 6 million people therecord.media The company said the threat actor gained access to a limited portion of its IT environment last month after compromising an employee account. By the end of April, Carnival determined that the attacker had copied…
- Live Nation confirms Ticketmaster breach after hackers hawk stolen info of 560 million therecord.media The company has confirmed that the leaked data was from a database hosted on Snowflake — one of the largest cloud storage companies.
- Hackers stole ‘nearly all’ call logs over six months from AT&T therecord.media The telecom giant said the massive breach involving logs from 2022 occurred through the third-party cloud platform Snowflake.
- Educational company McGraw Hill says Salesforce misconfiguration led to data leak therecord.media The data breach emerged this weekend when the ShinyHunters cybercriminal organization claimed to have stolen 45 million Salesforce records and threatened to leak the information by April 14 if a ransom was not paid.
- ADT says customer data stolen in cyber intrusion therecord.media The home security company ADT said cybercriminals breached company systems on Monday and stole a “limited set” of customer and prospective customer information.
- Hackers claim breach of Rockstar Games via cloud analytics platform therecord.media The ShinyHunters cybercrime group has claimed responsibility for breaching systems linked to video game developer Rockstar Games, threatening to release stolen data if a ransom is not paid.
- Hackers use PaperCut printer vulnerability to spread Clop ransomware therecord.media Hackers linked to the Clop ransomware operation are exploiting two recently-disclosed vulnerabilities in print management software PaperCut to steal corporate data from victims.
- Blue Yonder says November ransomware attack not connected to Cleo vulnerability therecord.media The Panasonic-owned company said it has no reason to believe recent claims from a cybercrime gang are connected to last month’s ransomware attack, which caused disruptions at Starbucks, BIC and several major supermarket…
- Experts warn of MOVEit Transfer tool exploitation using zero-day bug therecord.media Hackers are exploiting a new zero-day vulnerability affecting a popular file transfer tool used by thousands of major companies.
- In response to GoAnywhere attacks, Fortra says it has taken ‘multiple steps’ with customers, CISA therecord.media Fortra says it's working with customers and CISA to address cyberattacks using a vulnerability in its GoAnywhere managed file-transfer tool.
- Oil giant Shell discloses data breach linked to Accellion FTA vulnerability - ZDNET www.zdnet.com Updated: The information of stakeholders has been compromised.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Alex Martin (@AlexMartin) on X twitter.com UK Editor: @TheRecord_Media | Fellowship alumnus: @VirtualRoutes | @SkyNews | Agent: @NorthbankTalent
- Alexander Martin (@alexmartin.bsky.social) bsky.app Journalist covering cybersecurity and intelligence. UK Editor at The Record from Recorded Future News. Dad of two. 🏠 Sheffield 📧 [email protected] 📱 Signal: AlexanderMartin.79