BTC$85,190+0.77% LTC$69.87+3.93% XMR$543.25+0.03%
TorPortal TorPortalMarkets, mirrors, dark web news
News › Lea

News tagged CISA

Every TorPortal story that mentions CISA. 60 stories, newest first. Category: lea.

Latest coverage of CISA

Click a headline for the full story or jump to the original.

GitLab warns of critical RCE vulnerability in AI Gateway service
BleepingComputer · Oct 2, 2026 · 2 min read

GitLab warns of critical RCE vulnerability in AI Gateway service

GitLab warned customers today to immediately patch a critical AI Gateway vulnerability that could let attackers run arbitrary commands on vulnerable instances.
'Warlock' ransomware used in attacks on critical infrastructure in Portuguese, Spanish-speaking…
The Record · Oct 2, 2026 · 2 min read

'Warlock' ransomware used in attacks on critical infrastructure in Portuguese, Spanish-speaking countries

The group is exploiting a variety of vulnerabilities impacting Microsoft SharePoint, according to a new report from Symantec Threat Hunter Team.
Dell asks admins to patch max severity CSM flaws as soon as possible
BleepingComputer · Oct 2, 2026 · 2 min read

Dell asks admins to patch max severity CSM flaws as soon as possible

Dell has patched two maximum severity vulnerabilities in the Container Storage Modules (CSM) that connect Dell enterprise storage arrays to Kubernetes environments.
Fortinet warns of critical FortiMail flaw exploited in zero-day attacks
BleepingComputer · Oct 1, 2026 · 4 min read

Fortinet warns of critical FortiMail flaw exploited in zero-day attacks

Fortinet is warning customers of a critical FortiMail vulnerability, tracked as CVE-2026-104286, that is being actively exploited in zero-day attacks to execute unauthorized code or commands on vulnerable devices.
Google: Vulnerability disclosures double to 10,000 per month as AI fuels exploitation
The Record · Sep 30, 2026 · 3 min read

Google: Vulnerability disclosures double to 10,000 per month as AI fuels exploitation

Vulnerability disclosures continue to skyrocket, doubling over the course of the year to more than 10,000 each month, Google researchers warned.
CISA warns of critical pre-auth RCE flaw in MikroTik RouterOS
BleepingComputer · Sep 30, 2026 · 2 min read

CISA warns of critical pre-auth RCE flaw in MikroTik RouterOS

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is warning of a new critical vulnerability in MikroTik RouterOS that could lead to remote code execution or cause a denial-of-service condition.
Cisco warns of new SD-WAN zero-day exploited in attacks
BleepingComputer · Sep 30, 2026 · 2 min read

Cisco warns of new SD-WAN zero-day exploited in attacks

Cisco released security updates to address a critical zero-day in the Catalyst SD-WAN Manager (tracked as CVE-2026-76504) that attackers are actively exploiting to escalate to admin privileges.
US, UK warn of exploited Citrix NetScaler zero-day bugs
The Record · Sep 28, 2026 · 2 min read

US, UK warn of exploited Citrix NetScaler zero-day bugs

Incident responders began warning of potential vulnerabilities in NetScaler Gateway products on Saturday before cybersecurity agencies in the Netherlands, U.S. and U.K. released advisories on Sunday confirming vulnerabilities. Citrix…
CISA orders feds to patch exploited Citrix flaws by Wednesday
BleepingComputer · Sep 28, 2026 · 3 min read

CISA orders feds to patch exploited Citrix flaws by Wednesday

The Cybersecurity and Infrastructure Security Agency (CISA) has ordered U.S. government agencies over the weekend to secure their systems against attacks exploiting two critical Citrix NetScaler vulnerabilities.
Citrix confirms two NetScaler RCE zero-days exploited in attacks
BleepingComputer · Sep 27, 2026 · 4 min read

Citrix confirms two NetScaler RCE zero-days exploited in attacks

Citrix has confirmed that two critical NetScaler remote code execution vulnerabilities, tracked as CVE-2026-88771 and CVE-2026-88772, are being exploited in attacks and that it has released security updates to fix the flaws.
Kiteworks urges customers to stop using platform after warning from federal intelligence agencies
The Record · Sep 25, 2026 · 2 min read

Kiteworks urges customers to stop using platform after warning from federal intelligence agencies

Frank Balonis, CISO at Kiteworks, told Recorded Future News that the company “received credible threat intelligence from federal intelligence authorities indicating that a threat actor may attempt to target some Kiteworks systems for…
CISA warns of Sharepoint, WSO2, Adobe Commerce flaws exploited in attacks
BleepingComputer · Sep 25, 2026 · 2 min read

CISA warns of Sharepoint, WSO2, Adobe Commerce flaws exploited in attacks

The Cybersecurity and Infrastructure Security Agency (CISA) warns that hackers are exploiting a critical authentication bypass vulnerability (CVE-2026-5430) affecting multiple products from enterprise software provider WSO2.
FedRAMP VDR & VER: Daily Scans Are Only the Beginning
BleepingComputer · Sep 24, 2026 · 1 min read

FedRAMP VDR & VER: Daily Scans Are Only the Beginning

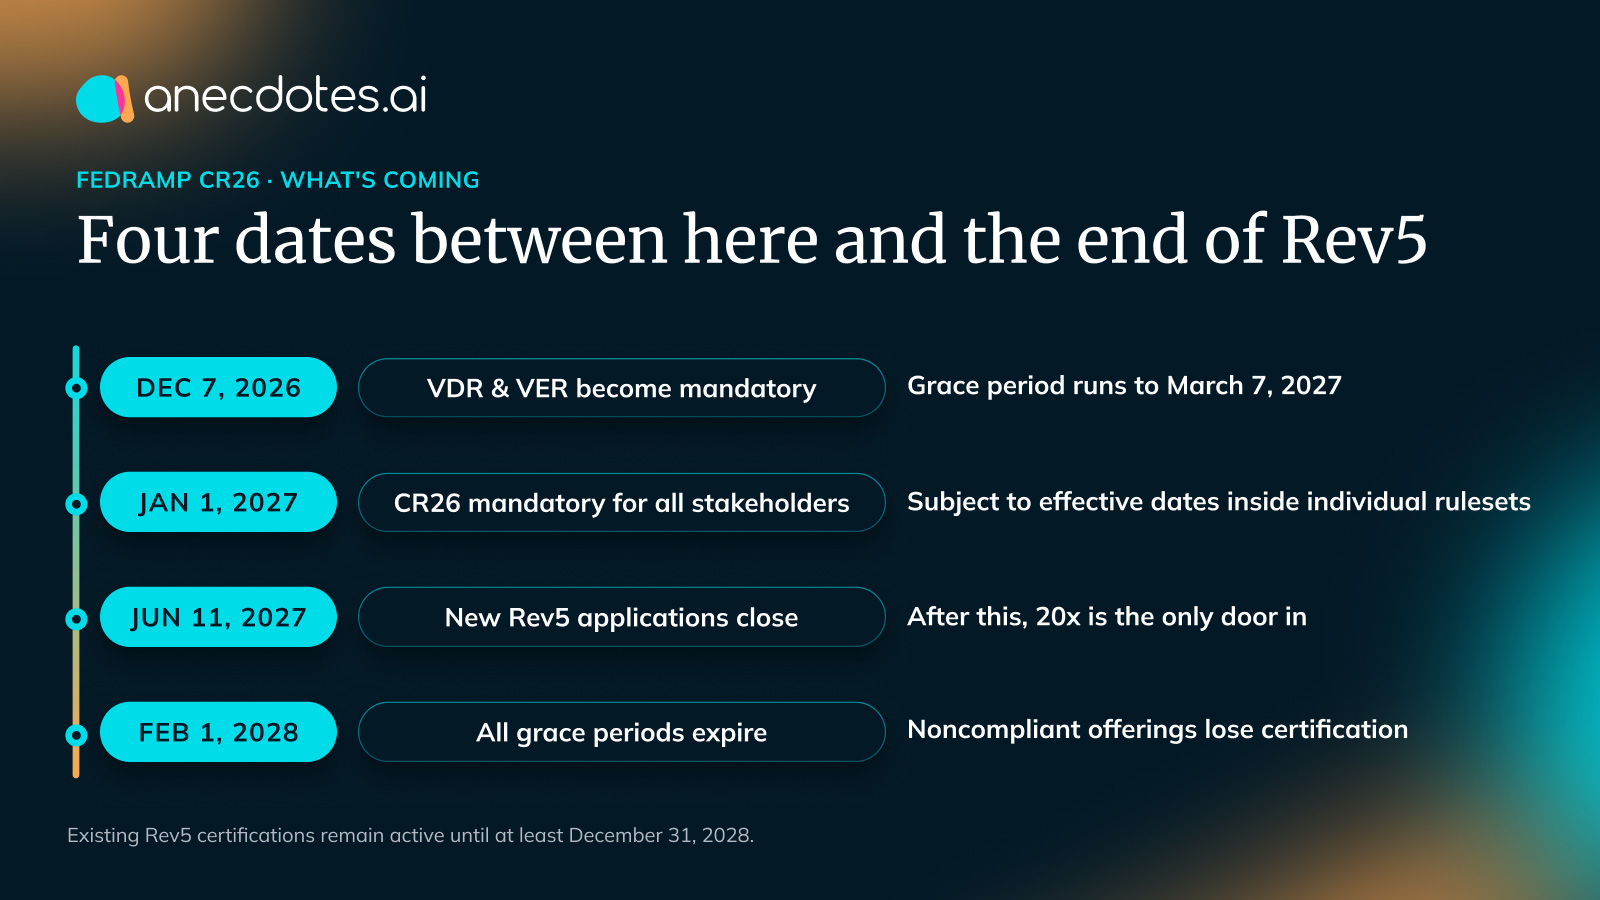
FedRAMP's new VDR and VER requirements make vulnerability management more continuous, with faster scanning, tighter remediation deadlines, and stronger evidence requirements. Anecdotes explains why the December 7 deadline is just the…
Hackers now exploit critical Roundcube flaw in code injection attacks
BleepingComputer · Sep 24, 2026 · 2 min read

Hackers now exploit critical Roundcube flaw in code injection attacks

A high-severity Roundcube Webmail vulnerability patched in May is now being actively exploited in attacks, according to the Canadian Centre for Cyber Security.
CISA: Ransomware gangs now exploiting critical TeamCity flaw
BleepingComputer · Sep 24, 2026 · 2 min read

CISA: Ransomware gangs now exploiting critical TeamCity flaw

​The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned federal agencies on Wednesday that ransomware gangs are now also exploiting a critical JetBrains TeamCity vulnerability patched in July.
Check Point warns of hackers exploiting Security Gateway VPN RCE flaw
BleepingComputer · Sep 23, 2026 · 2 min read

Check Point warns of hackers exploiting Security Gateway VPN RCE flaw

Cybersecurity company Check Point has confirmed active exploitation of CVE-2026-85102, a pre-authentication remote code execution (RCE) vulnerability in the VPN certificate-handling functionality of its Security Gateway product.
No evidence of successful foreign meddling in 2024 election, spy agencies found
The Record · Sep 23, 2026 · 4 min read

No evidence of successful foreign meddling in 2024 election, spy agencies found

U.S. intelligence officials found no evidence that any foreign adversary successfully interfered in the 2024 presidential election, according to sources familiar with the findings of a classified assessment.
InfraTrust report warns network management systems under attack
BleepingComputer · Sep 23, 2026 · 6 min read

InfraTrust report warns network management systems under attack

Attackers are increasingly targeting the management systems used to control enterprise infrastructure, with several critical vulnerabilities actively exploited before or shortly after vendors disclosed them.
Arista patches actively exploited VeloCloud Orchestrator zero-day
BleepingComputer · Sep 23, 2026 · 2 min read

Arista patches actively exploited VeloCloud Orchestrator zero-day

Arista Networks has released security patches for a zero-day flaw that is being actively exploited and affects VeloCloud Orchestrator (VCO) On-Prem deployments.
F5 patches BIG-IP APM zero-day flaw exploited in RCE attacks
BleepingComputer · Sep 23, 2026 · 2 min read

F5 patches BIG-IP APM zero-day flaw exploited in RCE attacks

F5 has released security updates to address a critical BIG-IP APM zero-day vulnerability being exploited in remote code execution attacks.
Chinese hackers exploit WordPress, Zyxel flaws to steal govt data
BleepingComputer · Sep 22, 2026 · 2 min read

Chinese hackers exploit WordPress, Zyxel flaws to steal govt data

A Chinese-speaking threat actor has been exploiting vulnerabilities in ZyXEL GS1900 Smart Managed Switches and WordPress to steal sensitive data from 996 devices and more than 18,500 records stored in backend databases.
Check Point warns of Management Server zero-day exploited in attacks
BleepingComputer · Sep 22, 2026 · 2 min read

Check Point warns of Management Server zero-day exploited in attacks

Check Point Software released emergency hotfixes to address a critical Security Management Server vulnerability that could let attackers run arbitrary scripts.
D-Link warns of max severity zero-day bug in DIR-822A routers
BleepingComputer · Sep 22, 2026 · 2 min read

D-Link warns of max severity zero-day bug in DIR-822A routers

D-Link warned customers of a maximum-severity vulnerability (CVE-2026-86296) with public proof-of-concept (PoC) exploit code and no patch, affecting legacy DIR-822A dual-band Wi-Fi routers.
CISA orders feds to patch Zyxel flaw exploited for data theft
BleepingComputer · Sep 22, 2026 · 3 min read

CISA orders feds to patch Zyxel flaw exploited for data theft

​Attackers are now actively exploiting a high-severity vulnerability in Zyxel GS1900 series switches, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA).
CISA alerts of active exploitation of three Linux kernel flaws
BleepingComputer · Sep 21, 2026 · 2 min read

CISA alerts of active exploitation of three Linux kernel flaws

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is warning that hackers are exploiting three Linux kernel vulnerabilities, one of them rated critical.
Cisco warns of max severity ISE zero-day exploited in attacks
BleepingComputer · Sep 17, 2026 · 1 min read

Cisco warns of max severity ISE zero-day exploited in attacks

Cisco has released security updates to address a maximum-severity Identity Services Engine vulnerability that attackers are actively exploiting in the wild.
Critical ScreenConnect flaw now actively exploited in attacks
BleepingComputer · Sep 16, 2026 · 1 min read

Critical ScreenConnect flaw now actively exploited in attacks

Attackers now exploit a critical-severity ConnectWise ScreenConnect vulnerability in the wild, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA).
CISA: Critical VMware RCE flaw now exploited by ransomware gangs
BleepingComputer · Sep 15, 2026 · 1 min read

CISA: Critical VMware RCE flaw now exploited by ransomware gangs

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned security teams that ransomware gangs have now joined ongoing attacks exploiting a critical VMware vCenter vulnerability patched in July.
Cisco patches Secure Email Gateway zero-day exploited in attacks
BleepingComputer · Sep 15, 2026 · 1 min read

Cisco patches Secure Email Gateway zero-day exploited in attacks

Cisco warned customers to patch a critical Secure Email Gateway zero-day security flaw that threat actors have been exploiting in attacks.
CISA: Hackers now exploit max severity GitLab flaw in attacks
BleepingComputer · Sep 14, 2026 · 2 min read

CISA: Hackers now exploit max severity GitLab flaw in attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned that hackers are now exploiting a maximum-severity GitLab vulnerability in attacks.
GitLab urges users to patch max severity path traversal flaw
BleepingComputer · Sep 11, 2026 · 1 min read

GitLab urges users to patch max severity path traversal flaw

GitLab urged users on Thursday to patch their servers immediately against a maximum-severity path traversal vulnerability tracked as CVE-2026-85706.
CISA: WatchGuard RCE flaw now exploited in ransomware attacks
BleepingComputer · Sep 10, 2026 · 1 min read

CISA: WatchGuard RCE flaw now exploited in ransomware attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that ransomware gangs are also exploiting a critical WatchGuard Firebox firewall vulnerability, which it flagged as actively exploited in December.
Cisco confirms CVE-2026-20079 Secure FMC flaw exploited in attacks
BleepingComputer · Sep 9, 2026 · 1 min read

Cisco confirms CVE-2026-20079 Secure FMC flaw exploited in attacks

Cisco has confirmed that a maximum-severity authentication bypass vulnerability tracked as CVE-2026-20079 in its Secure Firewall Management Center (FMC) software is being actively exploited in attacks.
CISA head says agency must change quickly to prevent the 'worst that could happen'
The Record · Sep 9, 2026 · 2 min read

CISA head says agency must change quickly to prevent the 'worst that could happen'

CISA's cybersecurity, infrastructure security and emergency communications divisions are among the priorities as the agency fills vacancies created at the beginning of the Trump administration, acting director Nick Andersen says.
US says Chinese firms extracted billions of tokens from frontier AI models
BleepingComputer · Sep 9, 2026 · 1 min read

US says Chinese firms extracted billions of tokens from frontier AI models

U.S. cybersecurity and intelligence agencies say that six Chinese AI companies conducted industrial-scale distillation attacks on American frontier AI models since at least late 2024.
MFA's Weakest Link: Account Recovery Is the New Attack Path
BleepingComputer · Sep 9, 2026 · 5 min read

MFA's Weakest Link: Account Recovery Is the New Attack Path

MFA makes account takeover harder, but attackers are increasingly targeting the recovery processes used to reset passwords and authentication methods. Specops explains why stronger identity verification at the service desk is critical to…
Microsoft posts nearly 1,000 bugs for Patch Tuesday as CISA warns two being exploited
The Record · Sep 8, 2026 · 1 min read

Microsoft posts nearly 1,000 bugs for Patch Tuesday as CISA warns two being exploited

The new record total for Patch Tuesday is 973 vulnerabilities.
SAP warns of maximum severity 'OVERPASS' kernel vulnerability
BleepingComputer · Sep 8, 2026 · 1 min read

SAP warns of maximum severity 'OVERPASS' kernel vulnerability

SAP has addressed 20 vulnerabilities across multiple products in its September 2026 security updates, including a maximum-severity memory corruption flaw in the SAP Kernel code.
ConnectWise warns of new ScreenConnect flaw without patch
BleepingComputer · Sep 7, 2026 · 1 min read

ConnectWise warns of new ScreenConnect flaw without patch

ConnectWise has shared temporary mitigation measures for a new ScreenConnect Remote Access vulnerability that it plans to patch later this week.
N-able patches max severity N-central flaw amid ongoing attacks
BleepingComputer · Sep 7, 2026 · 1 min read

N-able patches max severity N-central flaw amid ongoing attacks

N-able has released an emergency hotfix for a maximum-severity remote code execution (RCE) flaw affecting its N-central remote monitoring and management (RMM) platform.
Critical Citrix NetScaler auth bypass now leveraged in attacks
BleepingComputer · Sep 4, 2026 · 2 min read

Critical Citrix NetScaler auth bypass now leveraged in attacks

Attackers have begun targeting a critical-severity Citrix NetScaler auth bypass flaw (CVE-2026-19490) in the wild, according to vulnerability intelligence company Previdian.
G7 urges organizations to prepare for quantum cyber threats
The Record · Sep 4, 2026 · 2 min read

G7 urges organizations to prepare for quantum cyber threats

In a joint advisory released Thursday, the G7 Cyber Security Working Group and the U.S. Cybersecurity and Infrastructure Security Agency, CISA, said organizations should begin moving to post-quantum cryptography now.
Plex warns users to patch security vulnerabilities immediately
BleepingComputer · Sep 3, 2026 · 1 min read

Plex warns users to patch security vulnerabilities immediately

Plex urged users this week to update their desktop clients and media servers immediately to patch multiple security vulnerabilities.
SonicWall warns of actively exploited SMA1000 zero-day flaws
BleepingComputer · Sep 2, 2026 · 1 min read

SonicWall warns of actively exploited SMA1000 zero-day flaws

SonicWall warned customers that threat actors are chaining two new SMA1000 zero-day vulnerabilities in remote code execution attacks.
Critical Langflow flaw exploited to steal OpenAI and AWS keys
BleepingComputer · Sep 1, 2026 · 1 min read

Critical Langflow flaw exploited to steal OpenAI and AWS keys

Threat actors are exploiting an unauthenticated remote code execution vulnerability (CVE-2026-0768) in Langflow, an open-source framework for building AI applications, to steal credentials, tokens, and keys.
Nearly 22,000 Microsoft Exchange servers vulnerable to hijack attacks
BleepingComputer · Sep 1, 2026 · 2 min read

Nearly 22,000 Microsoft Exchange servers vulnerable to hijack attacks

Nearly 22,000 Microsoft Exchange servers exposed online remain unpatched against a high-severity authentication bypass vulnerability that allows attackers to hijack all user mailboxes.
Recently patched PaperCut zero-days used in data theft attacks
BleepingComputer · Sep 1, 2026 · 1 min read

Recently patched PaperCut zero-days used in data theft attacks

Two security vulnerabilities in the PaperCut NG and MF print management software, patched last week after being exploited as zero-days, are now being abused in data theft attacks.
Critical cPanel Flaw Could Expose Server Root Access
DarkDotWeb · Aug 31, 2026 · 2 min read

Critical cPanel Flaw Could Expose Server Root Access

A critical cPanel vulnerability lets certain authenticated users create arbitrary files and potentially execute code with root privileges.
PaperCut warns of hackers using printer management software flaw in attacks
The Record · Aug 28, 2026 · 2 min read

PaperCut warns of hackers using printer management software flaw in attacks

PaperCut released an emergency advisory on Thursday evening saying vulnerabilities in their print management software, PaperCut NG and MF, are under active exploitation.
AI Is Accelerating Vulnerability Discovery. Can Defenders Keep Up?
BleepingComputer · Aug 28, 2026 · 1 min read

AI Is Accelerating Vulnerability Discovery. Can Defenders Keep Up?

AI is accelerating vulnerability discovery, putting pressure on systems built to enrich, prioritize, and remediate flaws at a slower pace. Action1 explains why defenders increasingly need to correlate multiple intelligence sources and turn…
Over 8,300 Gitea servers vulnerable to code execution attacks
BleepingComputer · Aug 28, 2026 · 1 min read

Over 8,300 Gitea servers vulnerable to code execution attacks

Over 8,300 Internet-exposed Gitea instances are still unpatched against a critical security flaw exploited in ongoing remote code execution attacks, according to cybersecurity watchdog Shadowserver.
PaperCut warns of NG, MF flaw exploited in zero-day attacks
BleepingComputer · Aug 27, 2026 · 1 min read

PaperCut warns of NG, MF flaw exploited in zero-day attacks

PaperCut is warning that hackers are actively exploiting a vulnerability in all versions of its PaperCut NG and PaperCut MF print management software in zero-day attacks.
CISA orders feds to patch Citrix NetScaler RCE flaw by Saturday
BleepingComputer · Aug 27, 2026 · 2 min read

CISA orders feds to patch Citrix NetScaler RCE flaw by Saturday

CISA has ordered U.S. government agencies to patch their Citrix NetScaler appliances against an actively exploited remote code execution vulnerability by Saturday.
Hackers target Microsoft SharePoint RCE chain with PoC exploit
BleepingComputer · Aug 26, 2026 · 2 min read

Hackers target Microsoft SharePoint RCE chain with PoC exploit

Attackers are now targeting a chain of two Microsoft SharePoint vulnerabilities that can allow them to execute arbitrary code on unpatched servers, according to threat intelligence company Defused.
FBI disrupts proxy network enabling Chinese espionage operations
BleepingComputer · Aug 26, 2026 · 4 min read

FBI disrupts proxy network enabling Chinese espionage operations

The FBI has disrupted infrastructure associated with a technical "quartermaster" that provided reconnaissance, proxy management, and operational routing capabilities for Chinese cyber espionage activities.
Ubiquiti patches three max severity security vulnerabilities
BleepingComputer · Aug 26, 2026 · 1 min read

Ubiquiti patches three max severity security vulnerabilities

Ubiquiti has released security patches for three new maximum-severity vulnerabilities that threat actors can exploit remotely without privileges.
Hackers now exploit critical Gitea flaw in code injection attacks
BleepingComputer · Aug 26, 2026 · 2 min read

Hackers now exploit critical Gitea flaw in code injection attacks

Attackers are now exploiting a critical-severity vulnerability in the Gitea self-hosted Git service, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA).
Hackers breached over 270 Zimbra servers in ongoing attacks
BleepingComputer · Aug 25, 2026 · 1 min read

Hackers breached over 270 Zimbra servers in ongoing attacks

Threat actors have already compromised over 270 Zimbra instances in remote code execution attacks targeting a high-severity Zimbra Collaboration Suite (ZCS) vulnerability.
CISA orders urgent patching of actively exploited Zimbra flaw
BleepingComputer · Aug 24, 2026 · 1 min read

CISA orders urgent patching of actively exploited Zimbra flaw

The Cybersecurity and Infrastructure Security Agency (CISA) has ordered U.S. government agencies to patch an actively exploited vulnerability in Zimbra Collaboration Suite (ZCS) within three days.
Lawmakers call for investigation into impact of CISA staffing cuts
The Record · Aug 21, 2026 · 3 min read

Lawmakers call for investigation into impact of CISA staffing cuts

Lawmakers say little is known about how recent cuts have impacted CISA and how the knowledge that was lost has been replaced.
← All news