Australia arrests alleged TeamPCP hackers behind supply-chain attacks
Australian authorities have arrested and charged two young men accused of being part of the TeamPCP hacking group linked to a string of far-reaching developer supply chain attacks.
TeamPCP is a hacking group known for widespread supply-chain attacks over the past year that targeted open-source software and developer platforms to steal credentials, authentication secrets, and source code.
High-profile attacks attributed to TeamPCP have impacted Trivy, LiteLLM, Telnyx, SAP, and TanStack packages, while the group has also breached the European Commission, Mistral AI, OpenAI, and GitHub.
To carry out their attacks, the threat actors injected malicious code into software hosted on open-source repositories, which developers then unknowingly incorporated into their own applications on systems used by government, academic, and private-sector organizations.
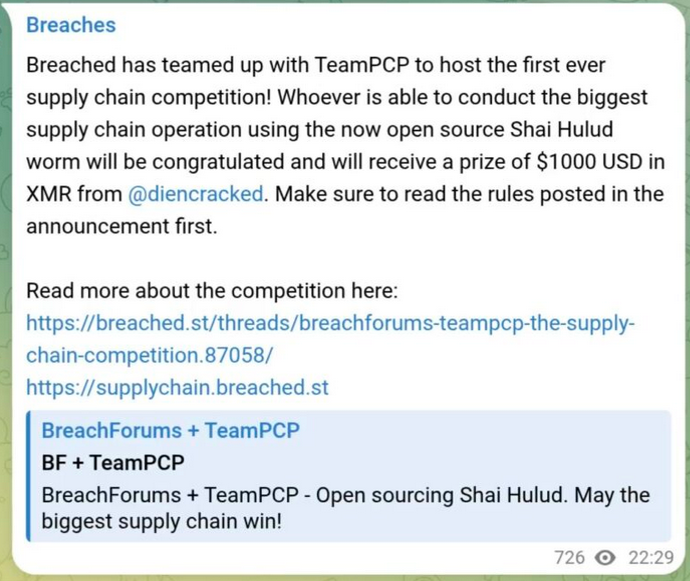
Rather than a cohesive group, the malicious activity is believed to have been carried out by a loose-knit collective of threat actors who all frequent the same hacking forums, Discord servers, and Telegram channels.
According to the Australian Federal Police (AFP), the FBI, and Western Australia Police, malicious code distributed by TeamPCP has potentially compromised over a thousand organizations worldwide, enabling the theft of half a million credentials and the exfiltration of at least 300GB of data.
"The alleged compromise of a small number of trusted software components had a significant global impact," reads the AFP announcement.
"To date, the financial impact includes global remediation costs estimated to be hundreds of millions of dollars."
The investigation began in April 2026, after the AFP and FBI received key information from cybersecurity firms.
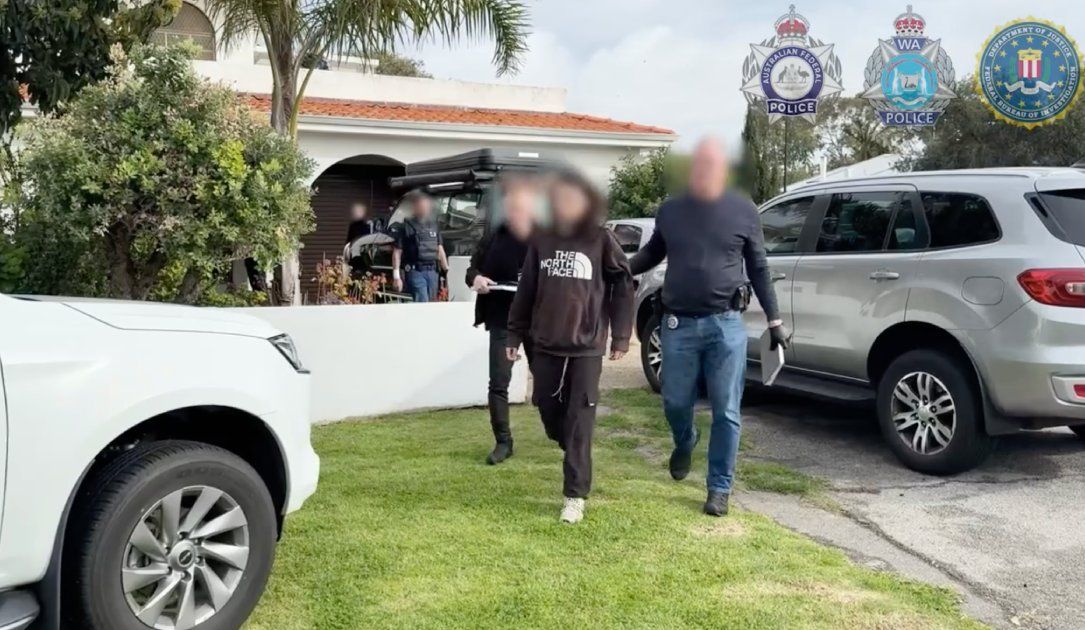
The two men, aged 21 and 23, were arrested in the western Australian cities of Cottesloe and Mandurah on August 26, 2026.
Photographs of the two arrestsSource: AFP
During the law enforcement action, investigators also seized electronic devices and other evidence for forensic analysis.
Police allege the two men received an undisclosed amount in cryptocurrency payments for their involvement in TeamPCP operations.
After the arrests were announced, both Flare and Brian Krebs published separate investigations detailing how Telegram activity, reused aliases, accounts, and other online traces linked alleged TeamPCP members to real-world identities.
The two suspects now face a combined 14 charges related to possessing and supplying data for computer offenses and modifying data to facilitate serious crimes.
The younger of the two also faces charges for allegedly dealing with at least $100,000 in criminal proceeds and failing to comply with an order requiring access to electronic data. The charges carry maximum penalties of 3 to 20 years' imprisonment per charge.
The AFP said further arrests or charges have not been ruled out at this stage, as it examines seized evidence.
References in this story
- Trivy vulnerability scanner breach pushed infostealer via GitHub Actions www.bleepingcomputer.com The Trivy vulnerability scanner was compromised in a supply-chain attack by threat actors known as TeamPCP, which distributed credential-stealing malware through official releases and GitHub Actions.
- Popular LiteLLM PyPI package backdoored to steal credentials, auth tokens www.bleepingcomputer.com The TeamPCP hacking group continues its supply-chain rampage, now compromising the massively popular "LiteLLM" Python package on PyPI and claiming to have stolen data from hundreds of thousands of devices during the…
- Backdoored Telnyx PyPI package pushes malware hidden in WAV audio www.bleepingcomputer.com TeamPCP hackers compromised the Telnyx package on the Python Package Index today, uploading malicious versions that deliver credential-stealing malware hidden inside a WAV file.
- Official SAP npm packages compromised to steal credentials www.bleepingcomputer.com Multiple official SAP npm packages were compromised in what is believed to be a TeamPCP supply-chain attack to steal credentials and authentication tokens from developers' systems.
- GitHub links repo breach to TanStack npm supply-chain attack www.bleepingcomputer.com GitHub says the hackers who breached 3,800 internal repositories gained access via a malicious version of the Nx Console VS Code extension, compromised in last week's TanStack npm supply-chain attack.
- CERT-EU: European Commission hack exposes data of 30 EU entities www.bleepingcomputer.com The European Union's Cybersecurity Service (CERT-EU) has attributed the European Commission cloud hack to the TeamPCP threat group, saying the resulting breach exposed the data of at least 29 other Union entities.
- TeamPCP hackers advertise Mistral AI code repos for sale www.bleepingcomputer.com The TeamPCP hacker group is threatening to leak source code from the Mistral AI project unless a buyer is found for the data.
- OpenAI confirms security breach in TanStack supply chain attack www.bleepingcomputer.com OpenAI says two employees' devices were breached in the recent TanStack supply chain attack that impacted hundreds of npm and PyPI packages, causing the company to rotate code-signing certificates for its applications…
- GitHub investigates internal repositories breach claimed by TeamPCP www.bleepingcomputer.com GitHub is investigating a breach of its internal repositories after the TeamPCP hacker group claimed to have accessed approximately 4,000 repositories containing private code.
- AI Threat Readiness 101 | Wiz wiz.io Learn the 4 pillars of AI Threat Readiness and how leading organizations use continuous validation, automated remediation, and AI-powered security operations .
- Two WA men charged following AFP-FBI-WAPF disruption of alleged global cybercrime syndicate | Australian Federal Police www.afp.gov.au Two West Australian men have been charged following a joint investigation between the AFP and Western Australia Police Force (WAPF), working in parallel with the Federal Bureau of Investigation (FBI), into a…
- Unmasking TeamPCP: Software Supply Chain Attacks - Flare flare.io Flare's Emerging Threats Team walks through the deanonymization of TeamPCP, a prolific threat actor behind major software supply chain attacks.
- Two Alleged ‘TeamPCP’ Hackers Arrested in Australia – Krebs on Security krebsonsecurity.com