DOJ: Gootloader used in at least 44 ransomware attacks costing $29 million since 2018
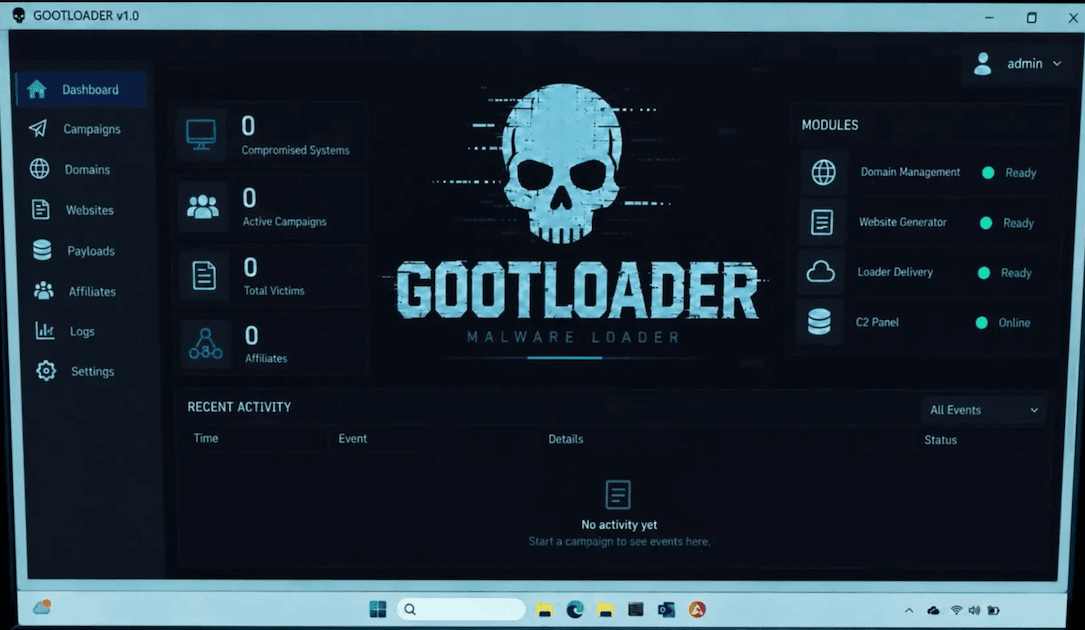
The Justice Department provided more details on the international law enforcement operation that took down the systems underpinning the Gootloader malware.
On Thursday, an international coalition of law enforcement agencies and cybersecurity companies dismantled more than 100 servers used by the StealC password-stealing malware as part of a wider takedown that disrupted 235 servers and 257 domains also used by the Gootloader and CastleRAT malware strains.
In a follow up notice on the operation later on Thursday, Assistant Attorney General A. Tysen Duva said the Justice Department removed Gootloader from more than 100 servers, including compromised websites, and seized several domain names that the cybercriminals used to deliver and control the Gootloader malware.
FBI Cyber Branch Operations Director Brett Leatherman said hackers used the network of compromised websites to infect thousands of computers with Gootloader, providing them with the access needed to deploy ransomware.
Justice Department officials said Gootloader has existed since 2018 and was used to infect 25,000 devices globally. In court documents unsealed this week, prosecutors said victims typically downloaded Gootloader accidentally, adding their compromised device to a botnet of other infected computers.
The hackers then sold access to the network of devices to ransomware gangs.
The DOJ said more than 44 U.S.-based ransomware victims were initially infected by Gootloader — leading to a total of $28.8 million in losses.
Leatherman said they were able to disrupt the Gootloader network of compromised devices through coordinated technical operations, victim notifications and remediation.
“The Gootloader malware targeted victims on a global scale, including attacks on the U.S. Department of War and the Defense Industrial Base,” Defense Department official Kenneth DeChellis said in a statement.
The Shadowserver Foundation worked with internet service providers and Computer Security Incident Response Teams globally to identify infected systems and notify victims. Compromised domains now carry a seizure banner.
The Justice Department said the takedowns were part of Operation Endgame — a long-running international law enforcement initiative aimed at disrupting powerful malware strains and massive botnets.
Previous parts of the operation took down servers, websites and botnets tied to malware strains like DanaBot, IcedID, SystemBC, Pikabot, SmokeLoader, Bumblebee and Trickbot. Operation Endgame also saw the takedown of the Rhadamanthys infostealer, the VenomRAT remote access trojan and the Elysium botnet.
Last year, the Justice Department also partnered with other agencies to take down AVCheck.net, Crypt.guru, Cryptor.live and Cryptor.biz — sites used to test malware against real antivirus tools.
References in this story
- European authorities take down SteaIC malware servers for second time this year therecord.media German authorities on Thursday said investigators traced the rebuilt network to the Virtualine bulletproof hosting provider, seized by the FBI in October, with the assistance of police in Frankfurt and the Dutch…
- Gootloader Malware Disrupted in International Cyber Operation www.justice.gov
- International operation takes down crypting sites used for testing malware therecord.media The sites were used for more than a decade by cybercriminals who wanted to test malware against security tools.
- Over 100 malware servers shut down in 'largest ever' operation against botnets therecord.media Europol and other authorities said they disrupted malware families such as IcedID, SystemBC, Pikabot, SmokeLoader, Bumblebee and Trickbot.
- Operation Endgame: Police reveal takedowns of three key cybercrime tools therecord.media The Rhadamanthys infostealer, the VenomRAT remote access trojan and the Elysium botnet were targeted in the latest phase of the international police action known as Operation Endgame.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- jon greig (@jgreigj) on X twitter.com @TheRecord_Media cybersecurity reporter. formerly @zdnet @cambodiadaily @haitiantimes_ — send tips to [email protected] or signal: jgreig.51
- jon greig (@jgreig.bsky.social) bsky.app cybersecurity reporter for The Record. formerly: zdnet, techrepublic, blavity, haitian times, cambodia daily — send tips to [email protected] or signal: jgreig.51