Binance Warns of iOS Flaw Exposing Crypto Wallet Keys
Binance warns that a public iOS sandbox escape could let malicious apps access private files, including cryptocurrency wallet keys.
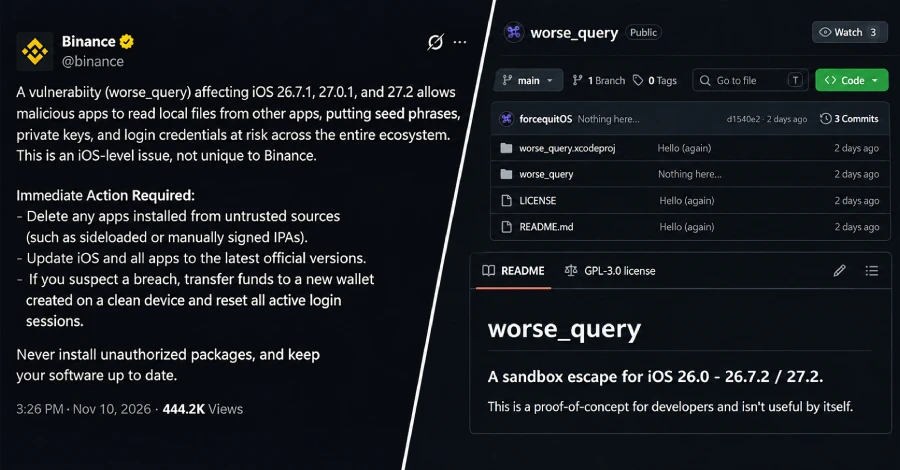
Cryptocurrency exchange Binance has warned iPhone users about a publicly disclosed iOS vulnerability that could allow malicious applications to access files belonging to other apps, potentially exposing sensitive information such as cryptocurrency recovery phrases, private keys and login credentials.
The vulnerability, known as worse_query, was publicly released on GitHub by security researchers using the names forcequit and 0xjohnny. Binance warned on November 10 that the issue affects specific versions of iOS 26 and iOS 27, including versions 26.7.1, 27.0.1 and 27.2.
According to Binance, the problem exists within Apple‘s operating system and is not limited to its own application. Any application storing sensitive information locally could potentially be affected if a malicious app manages to exploit the vulnerability.
The researchers’ proof-of-concept demonstrates how an application can bypass normal iOS sandbox restrictions and access other applications’ data containers. On iOS 27, the technique can also reach certain system folders.
The exploit relies on an App Group container, a feature normally used by applications to share data with related apps. The researcher behind worse_query has described the released code as a development tool rather than a complete standalone attack. However, other developers have already built applications around the technique.
One example is WQ Files, a file manager developed by Christoph Kolbicz. The application uses worse_query to access data belonging to other apps without requiring a jailbroken device or a kernel exploit. Its capabilities reportedly include browsing, exporting, editing and deleting files from those data containers.
WQ Files can be installed through sideloading services such as AltStore and SideStore. These tools allow users to install applications outside Apple’s official App Store. This creates a potential risk if a malicious application using the technique is installed on an affected device.
Binance has advised users to remove unnecessary applications and anything installed from untrusted sources. The exchange also recommends installing the latest official versions of iOS and all applications.
For users who believe their devices may already have been compromised, Binance recommends creating a new cryptocurrency wallet on a clean device, transferring funds to it and resetting active login sessions.
There is still uncertainty surrounding Apple’s response. The company released iOS 27.2.1 and iOS 26.7.3 on November 9, addressing several security issues, but the accompanying security notes do not specifically mention worse_query or confirm that the sandbox escape has been resolved.
Neither Binance nor the researchers have reported confirmed cases of attackers exploiting worse_query to access cryptocurrency wallets or steal funds. No specific wallet application has been publicly identified as compromised through the technique.
For now, the public availability of the exploit and the possibility of accessing sensitive application data make it a concern for iPhone users, particularly those who store cryptocurrency credentials or other valuable information on their devices. Until Apple clarifies whether the vulnerability has been addressed, users should be cautious about installing applications from outside trusted sources.
Source: The Hacker News
References in this story
- www.binance.com
- App Store www.apple.com The App Store gives people around the world a safe and trusted place to discover apps that meet our high standards for privacy, security, and content.
- Binance Warns of iOS Sandbox Escape That Could Expose Crypto Wallet Keys, No Fix Confirmed thehackernews.com Binance warns that an iOS sandbox escape could expose crypto wallet keys to malicious apps, with no confirmed fix in Apple's latest updates.