Russian and Ukrainian hackers hijack emergency apps to spread fake nuclear attack warnings
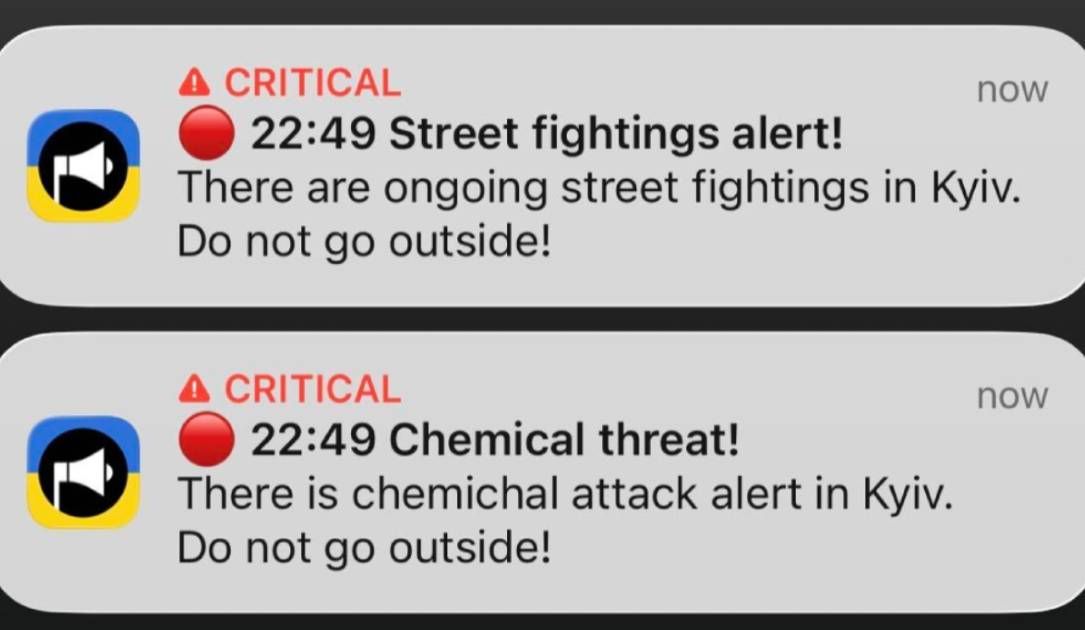
KYIV, Ukraine — Late on Sunday, Kyiv residents received alarming notifications on their phones warning of possible radiation hazard, a chemical threat and ongoing street fighting in the Ukrainian capital.
The warnings came from an app that millions of Ukrainians count on as a reliable source of alerts about incoming Russian missiles and drones. But this time, the threats were fake, and the app itself appeared to have been compromised by hackers.
Ukraine's Air Force quickly warned that the officially supported Air Alert app had "likely been compromised by the enemy" and urged residents to disregard the messages.
A Recorded Future News reporter received several of the notifications, which appeared genuine and even featured the familiar voice used by the app to announce emergencies.
One message, written in Russian, warned of a possible strike involving Russia’s Oreshnik, a ballistic missile capable of carrying nuclear warheads. It also contained a link to a Telegram channel associated with a previously unknown hacking group calling itself Hitcore Corp, which claimed responsibility for the breach.
The app's developers subsequently disabled push notifications and temporarily suspended the service.
"Today, unauthorized individuals interfered with the app's operation," the developers said in a statement Sunday. They added that the app does not store personal information and urged users not to open links contained in suspicious notifications.
By early Monday, the developers said they had begun gradually restoring the service. Push notifications and basic threat indicators were operational again, although the display of incoming threats on the app's map remained temporarily disabled. The team said it was implementing additional security measures to prevent similar attacks.
Ukrainian authorities moved quickly to reassure residents that the country's broader emergency warning infrastructure had not been affected.
Ukraine's Center for Countering Disinformation dismissed the false alerts and warned against sharing unverified information. The State Emergency Service said the national warning system continued to operate normally, while Kyiv authorities confirmed that the city's separate Kyiv Digital app remained functional.
The Air Alert app was launched in 2022, shortly after Russia's full-scale invasion, with support from Ukraine's Ministry of Digital Transformation. Developed by Ukrainian security technology company Ajax Systems, it had 6.6 million active users as of January 2026.
The app allows users to receive warnings about missile and drone attacks, chemical hazards and other emergencies in their chosen region, even when their phones are set to silent mode. The cyberattack on the app came as Ukrainian authorities warned of another possible large-scale Russian strike in the coming days, potentially targeting Kyiv's energy infrastructure.
Digital retaliation
Hours after the Ukrainian app was compromised, hackers from a group calling itself DC8044 claimed responsibility for a cyberattack on a mobile app operated by Russia's Ministry of Emergency Situations, known as EMERCOM.
The group, which describes itself as an independent cybersecurity and hacking community based in Kyiv, said it had gained access to the Russian app through its application programming interface, or API, and published technical details of the alleged intrusion on its Telegram channel.
According to the hackers, they used the compromised system to distribute false warnings claiming that nuclear warheads had been launched toward Russia. The messages also urged residents to stockpile food and take shelter in basements. False warnings appeared on channels associated with the ministry and regional emergency response centers, according to reports of the incident.
Russia's Emergency Situations Ministry acknowledged Monday that its mobile app had been hacked but insisted that the country's primary public warning infrastructure was unaffected.
"The hacking of the mobile app has not affected and cannot affect the operation of the public warning system," the ministry said.
It said emergency notifications would continue to be delivered through sirens, loudspeakers, text messages, television and radio broadcasts, while the compromised app served only as a supplementary source of information.
These were not the first attempts to exploit emergency alert systems during the war.
In 2023, hackers reportedly compromised broadcasting infrastructure used by several Russian commercial radio stations, interrupting programming with fabricated warnings of imminent air raids and missile strikes. Listeners were instructed to seek shelter immediately.
Similar tactics have also been used outside the Russia-Ukraine conflict. Also in 2023, cybersecurity company Group-IB reported that the hacktivist group AnonGhost had compromised Red Alert, an Israeli mobile app that provides real-time warnings of incoming rocket attacks. The attackers were reportedly able to send unauthorized notifications to some users, including a fabricated warning about a nuclear bomb.
References in this story
- Повітряні Сили ЗС України / Air Force of the Armed Forces of Ukraine t.me ❗️Увага Імовірно додаток «Повітряна тривога» піддався ворожому впливу. Жодної радіаційної загрози немає! Зберігайте спокій, слідкуйте за нашими повідомленнями на нашому каналі!
- Повітряна Тривога t.me Сьогодні сторонні особи здійснили несанкціоноване втручання в роботу застосунку. Ми відключили пуш-сповіщення та тимчасово призупинили роботу застосунку. Застосунок не зберігає персональних даних, тож загрози для…
- Повітряна Тривога t.me Поступово повертаємо в роботу застосунок «Повітряна тривога» після кібератаки. Наразі на карті доступна інформація про жовтий і червоний рівні небезпеки (дронова і масована дронова/ракетна відповідно). Також приходять…
- ЦЕНТР ПРОТИДІЇ ДЕЗІНФОРМАЦІЇ t.me ❗️Додаток «Повітряна тривога», ймовірно, зазнав злому. Наразі інформація, що поширюється щодо рівнів загроз, не відповідає дійсності. Закликаємо не панікувати, не переходити за жодними сторонніми посиланнями та не…
- ДСНС України t.me ‼️ Офіційне повідомлення ДСНС щодо роботи систем оповіщення Загальнодержавна система оповіщення працює в штатному режимі. Всі сигнали про загрози передаються до обласних адміністрацій та, відповідно, до вуличних систем…
- КМДА – офіційний канал t.me 📢 Застосунок Київ Цифровий і вулична система оповіщення в столиці працюють у штатному режимі та сповіщатимуть про повітряну тривогу в разі виникнення загрози. Наразі в Києві повітряної тривоги немає 📲 Інформація про…
- 400 Bad Request www.kmu.gov.ua
- Звіт Ajax Systems за 2025 рік | Ajax Press Page ajax.systems Стаття на тему «Звіт Ajax Systems за 2025 рік» від експертів Ajax Systems | Ajax Press Page
- DC8044 F33d t.me В ответ на взлом неофициального популярного приложения по оповещению украинцев о воздушных тревогах, неравнодушные подписчики DC8044 развалили систему оповещения МЧС рф, результат чего вчера наблюдала вся россия во всех…
- ASTRA t.me Взломана единая государственная система предупреждения и ликвидации чрезвычайных ситуаций Российской Федерации, — СМИ «Враг взломал официальное приложение "МЧС России" и все региональные каналы ведомства в мессенджере…
- Система оповещения населения Российской Федерации функционирует в штатном режиме - Новости mchs.gov.ru Система оповещения населения Российской Федерации функционирует в штатном режиме - Новости - МЧС России
- Russia blames hackers as commercial radio stations broadcast fake air strike warnings therecord.media Fake air raid and missile strike warnings blared from Russian radio stations. Officials blamed the incident on a hack of satellite tech.
- Group-IB Threat Intelligence (@GroupIB_TI) on X x.com On Sunday, #AnonGhost, a well-known #hacktivist group, exploited an API vulnerability in the #RedAlert app, that provides real-time rocket alerts for Israelis. In their exploit, they successfully intercepted requests…
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Daryna Antoniuk (@darynant.bsky.social) bsky.app Cybersecurity Reporter at Recorded Future News. Ex at The Kyiv Independent/Forbes/The Kyiv Post 📍Kyiv, Ukraine