China’s FamousSparrow hackers target Latin America with new backdoor
Alleged Chinese hackers are breaking into government agencies across Latin America using a new backdoor that researchers are calling “SparroWocky.”
ESET researcher Alexandre Côté Cyr said he has been following the campaign since at least August 2025 and tracked attacks on government departments in Guatemala, Honduras, Puerto Rico, Panama, Venezuela, Peru and Argentina.
Côté Cyr added that the campaign is a “rare occurrence” because typically Chinese government-backed hacking campaigns, particularly ones that have lasted this long, target multiple regions.
In a lengthy report about SparroWocky, ESET theorized that China’s focus on Latin America is tied to U.S. President Donald Trump’s renewed focus on the region since taking office last year. His administration has directly targeted long-term investments China has cultivated in the region.
ESET said the campaign, attributed to a long-running Chinese operation known as FamousSparrow, is likely “intended to help China better monitor and anticipate the reaction of local governments to current U.S. pressures.”
One of the organizations attacked in Panama is directly involved in an ongoing commercial dispute over two major ports located in the canal area. Trump has taken issue with Chinese companies operating some of the ports and has sought to disrupt Beijing’s alleged control over parts of the canal.
‘Jabberwocky’
ESET named the malware SparroWocky because the first samples of the backdoor all contained the opening stanza of “Jabberwocky,” a poem by English author Lewis Carroll.
The backdoor is designed to stymie analysis and shows the group has a deep knowledge of internal Windows systems. The malware incorporates code from open-source projects, according to ESET.
It allows users to exfiltrate files and take screenshots while also collecting information about the compromised system, including the IP address, usernames and more.
FamousSparrow has been operating since at least 2019, conducting Chinese cyberespionage campaigns in multiple regions through a variety of vulnerabilities. The group originally targeted hotels but evolved to breach governments, trade groups, international organizations and law firms.
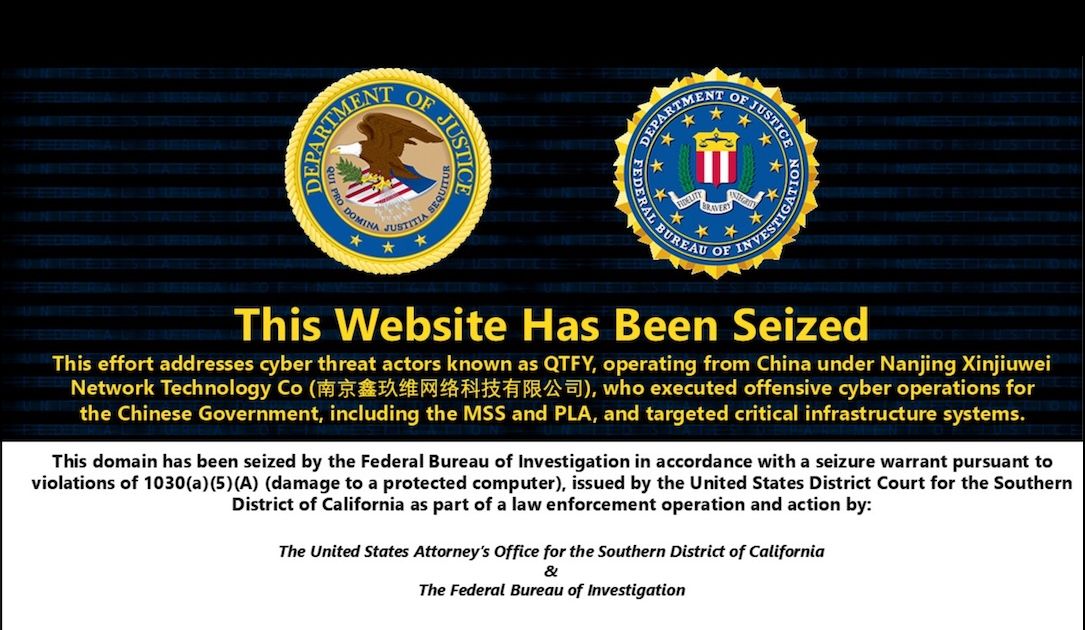
ESET said FamousSparrow has been publicly linked to Salt Typhoon, a Chinese group that U.S. law enforcement agencies accused of breaching the Treasury Department, several large U.S. telecoms and an email platform used by Congressional staffers.
References in this story
- Beware the SparroWock: The backdoor that bites, the commands that catch www.welivesecurity.com ESET researchers document SparroWocky, the new flagship backdoor of the FamousSparrow APT group
- A new APT is targeting hotels across the world therecord.media A new advanced persistent threat (APT), a term used to describe state-sponsored cyber-espionage groups, has been spotted mounting attacks against hotels across the world.
- ToolShell bug used by Chinese attackers against governments in Africa, South America therecord.media Government agencies in African and South American nations are on the long list of organizations breached through exploitation of a vulnerability in Microsoft SharePoint, incident responders revealed.
- Chinese ‘FamousSparrow’ hackers back from the dead and targeting North America, researchers say therecord.media Thought to be dormant since 2022, the group is now believed to have been targeting organizations in the U.S., Mexico and Honduras.
- CISA: Treasury was only federal agency impacted by recent China breach therecord.media The Cybersecurity and Infrastructure Security Agency said in a short statement that there is “no indication that any other federal agencies" have been impacted by a breach of Treasury Department systems attributed to…
- At least 8 US telcos, dozens of countries impacted by Salt Typhoon breaches, White House says therecord.media Senators briefed on the wide-ranging breaches by Chinese hackers called for action on Wednesday to protect the country's telecommunications networks.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- Advanced Cyber Threat Intelligence | Recorded Future www.recordedfuture.com Get real-time, actionable cyber threat intelligence with Recorded Future. Mitigate cyber risks, prioritize threats, and proactively secure your organization.
- jon greig (@jgreigj) on X twitter.com @TheRecord_Media cybersecurity reporter. formerly @zdnet @cambodiadaily @haitiantimes_ — send tips to [email protected] or signal: jgreig.51
- jon greig (@jgreig.bsky.social) bsky.app cybersecurity reporter for The Record. formerly: zdnet, techrepublic, blavity, haitian times, cambodia daily — send tips to [email protected] or signal: jgreig.51