The link you clicked points at a different website. We do not run that site and we cannot promise anything about what is on it. If you still want to go there, the button below opens it in a new tab.
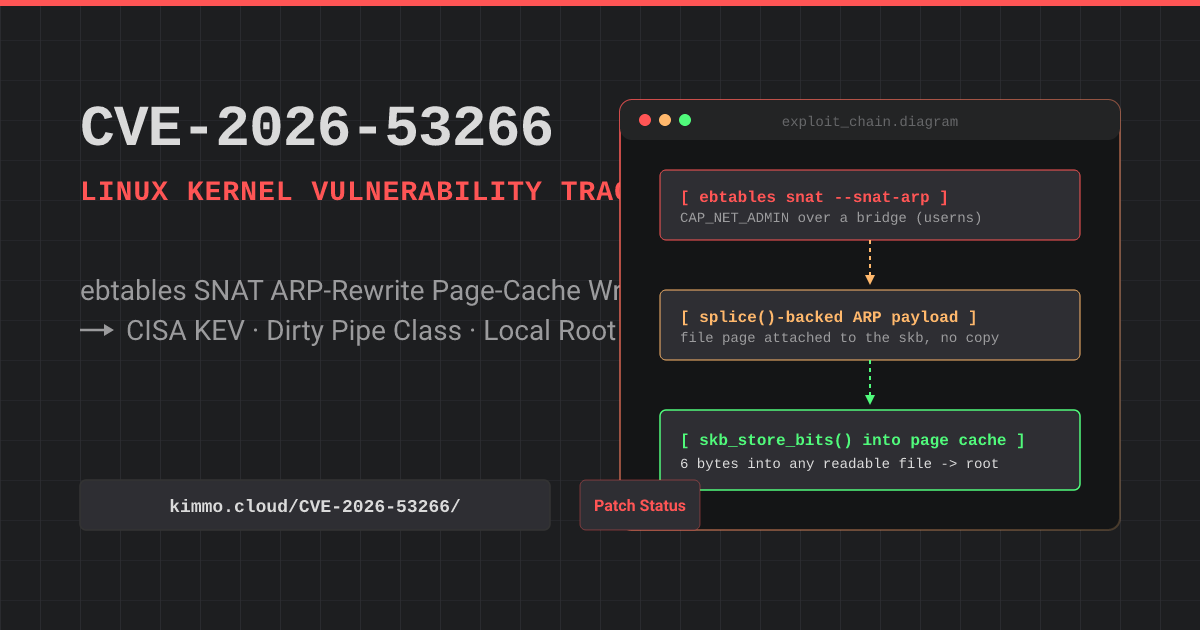
Linux kernel netfilter bridge ebtables SNAT ARP sender-address rewrite into a splice-backed file page (CVE-2026-53266) — a page-cache write, potential local privilege escalation, CISA KEV, fixed upstream since June 2026 — distro patch status tracker
If the address looks unfamiliar, close this tab and use the navigation above instead. TorPortal does not endorse third party sites and links inside news stories come straight from the source article.
